CVE-2024-27288 (GCVE-0-2024-27288)
Vulnerability from cvelistv5 – Published: 2024-03-06 18:23 – Updated: 2024-08-27 16:52- CWE-863 - Incorrect Authorization
| URL | Tags |
|---|---|
| https://github.com/1Panel-dev/1Panel/security/adv… | x_refsource_CONFIRM |
| https://github.com/1Panel-dev/1Panel/releases/tag… | x_refsource_MISC |
| Vendor | Product | Version | CPE status | |
|---|---|---|---|---|
| 1Panel-dev | 1Panel |
Affected:
< 1.10.1-lts
|
guessed | |
| fit2cloud | 1panel |
Affected:
0 , < 1.10.1-lts
(custom)
cpe:2.3:a:fit2cloud:1panel:*:*:*:*:*:*:*:* |
{
"containers": {
"adp": [
{
"providerMetadata": {
"dateUpdated": "2024-08-02T00:28:00.342Z",
"orgId": "af854a3a-2127-422b-91ae-364da2661108",
"shortName": "CVE"
},
"references": [
{
"name": "https://github.com/1Panel-dev/1Panel/security/advisories/GHSA-26w3-q4j8-4xjp",
"tags": [
"x_refsource_CONFIRM",
"x_transferred"
],
"url": "https://github.com/1Panel-dev/1Panel/security/advisories/GHSA-26w3-q4j8-4xjp"
},
{
"name": "https://github.com/1Panel-dev/1Panel/releases/tag/v1.10.1-lts",
"tags": [
"x_refsource_MISC",
"x_transferred"
],
"url": "https://github.com/1Panel-dev/1Panel/releases/tag/v1.10.1-lts"
}
],
"title": "CVE Program Container"
},
{
"affected": [
{
"cpes": [
"cpe:2.3:a:fit2cloud:1panel:*:*:*:*:*:*:*:*"
],
"defaultStatus": "unknown",
"product": "1panel",
"vendor": "fit2cloud",
"versions": [
{
"lessThan": "1.10.1-lts",
"status": "affected",
"version": "0",
"versionType": "custom"
}
]
}
],
"metrics": [
{
"other": {
"content": {
"id": "CVE-2024-27288",
"options": [
{
"Exploitation": "poc"
},
{
"Automatable": "no"
},
{
"Technical Impact": "partial"
}
],
"role": "CISA Coordinator",
"timestamp": "2024-08-27T16:50:21.682289Z",
"version": "2.0.3"
},
"type": "ssvc"
}
}
],
"providerMetadata": {
"dateUpdated": "2024-08-27T16:52:53.993Z",
"orgId": "134c704f-9b21-4f2e-91b3-4a467353bcc0",
"shortName": "CISA-ADP"
},
"title": "CISA ADP Vulnrichment"
}
],
"cna": {
"affected": [
{
"product": "1Panel",
"vendor": "1Panel-dev",
"versions": [
{
"status": "affected",
"version": "\u003c 1.10.1-lts"
}
]
}
],
"descriptions": [
{
"lang": "en",
"value": "1Panel is an open source Linux server operation and maintenance management panel. Prior to version 1.10.1-lts, users can use Burp to obtain unauthorized access to the console page. The vulnerability has been fixed in v1.10.1-lts. There are no known workarounds."
}
],
"metrics": [
{
"cvssV3_1": {
"attackComplexity": "LOW",
"attackVector": "NETWORK",
"availabilityImpact": "LOW",
"baseScore": 6.3,
"baseSeverity": "MEDIUM",
"confidentialityImpact": "LOW",
"integrityImpact": "LOW",
"privilegesRequired": "NONE",
"scope": "UNCHANGED",
"userInteraction": "REQUIRED",
"vectorString": "CVSS:3.1/AV:N/AC:L/PR:N/UI:R/S:U/C:L/I:L/A:L",
"version": "3.1"
}
}
],
"problemTypes": [
{
"descriptions": [
{
"cweId": "CWE-863",
"description": "CWE-863: Incorrect Authorization",
"lang": "en",
"type": "CWE"
}
]
}
],
"providerMetadata": {
"dateUpdated": "2024-03-06T18:23:50.053Z",
"orgId": "a0819718-46f1-4df5-94e2-005712e83aaa",
"shortName": "GitHub_M"
},
"references": [
{
"name": "https://github.com/1Panel-dev/1Panel/security/advisories/GHSA-26w3-q4j8-4xjp",
"tags": [
"x_refsource_CONFIRM"
],
"url": "https://github.com/1Panel-dev/1Panel/security/advisories/GHSA-26w3-q4j8-4xjp"
},
{
"name": "https://github.com/1Panel-dev/1Panel/releases/tag/v1.10.1-lts",
"tags": [
"x_refsource_MISC"
],
"url": "https://github.com/1Panel-dev/1Panel/releases/tag/v1.10.1-lts"
}
],
"source": {
"advisory": "GHSA-26w3-q4j8-4xjp",
"discovery": "UNKNOWN"
},
"title": "1Panel open source panel project has an unauthorized vulnerability."
}
},
"cveMetadata": {
"assignerOrgId": "a0819718-46f1-4df5-94e2-005712e83aaa",
"assignerShortName": "GitHub_M",
"cveId": "CVE-2024-27288",
"datePublished": "2024-03-06T18:23:50.053Z",
"dateReserved": "2024-02-22T18:08:38.873Z",
"dateUpdated": "2024-08-27T16:52:53.993Z",
"state": "PUBLISHED"
},
"dataType": "CVE_RECORD",
"dataVersion": "5.1",
"vulnerability-lookup:meta": {
"epss": {
"cve": "CVE-2024-27288",
"date": "2026-09-18",
"epss": "0.00471",
"percentile": "0.39854"
},
"fkie_nvd": {
"descriptions": [
{
"lang": "en",
"value": "1Panel is an open source Linux server operation and maintenance management panel. Prior to version 1.10.1-lts, users can use Burp to obtain unauthorized access to the console page. The vulnerability has been fixed in v1.10.1-lts. There are no known workarounds."
},
{
"lang": "es",
"value": "1Panel es un panel de gesti\u00f3n de operaci\u00f3n y mantenimiento de servidores Linux de c\u00f3digo abierto. Antes de la versi\u00f3n 1.10.1-lts, los usuarios pod\u00edan usar Burp para obtener acceso no autorizado a la p\u00e1gina de la consola. La vulnerabilidad se ha solucionado en v1.10.1-lts. No se conocen workarounds."
}
],
"id": "CVE-2024-27288",
"lastModified": "2024-11-21T09:04:15.310",
"metrics": {
"cvssMetricV31": [
{
"cvssData": {
"attackComplexity": "LOW",
"attackVector": "NETWORK",
"availabilityImpact": "LOW",
"baseScore": 6.3,
"baseSeverity": "MEDIUM",
"confidentialityImpact": "LOW",
"integrityImpact": "LOW",
"privilegesRequired": "NONE",
"scope": "UNCHANGED",
"userInteraction": "REQUIRED",
"vectorString": "CVSS:3.1/AV:N/AC:L/PR:N/UI:R/S:U/C:L/I:L/A:L",
"version": "3.1"
},
"exploitabilityScore": 2.8,
"impactScore": 3.4,
"source": "security-advisories@github.com",
"type": "Secondary"
}
]
},
"published": "2024-03-06T19:15:07.933",
"references": [
{
"source": "security-advisories@github.com",
"url": "https://github.com/1Panel-dev/1Panel/releases/tag/v1.10.1-lts"
},
{
"source": "security-advisories@github.com",
"url": "https://github.com/1Panel-dev/1Panel/security/advisories/GHSA-26w3-q4j8-4xjp"
},
{
"source": "af854a3a-2127-422b-91ae-364da2661108",
"url": "https://github.com/1Panel-dev/1Panel/releases/tag/v1.10.1-lts"
},
{
"source": "af854a3a-2127-422b-91ae-364da2661108",
"url": "https://github.com/1Panel-dev/1Panel/security/advisories/GHSA-26w3-q4j8-4xjp"
}
],
"sourceIdentifier": "security-advisories@github.com",
"vulnStatus": "Awaiting Analysis",
"weaknesses": [
{
"description": [
{
"lang": "en",
"value": "CWE-863"
}
],
"source": "security-advisories@github.com",
"type": "Secondary"
}
]
},
"nvd": {
"cve": {
"affected": [
{
"affectedData": [
{
"product": "1Panel",
"vendor": "1Panel-dev",
"versions": [
{
"status": "affected",
"version": "\u003c 1.10.1-lts"
}
]
}
],
"source": "security-advisories@github.com"
},
{
"affectedData": [
{
"cpes": [
"cpe:2.3:a:fit2cloud:1panel:*:*:*:*:*:*:*:*"
],
"defaultStatus": "unknown",
"product": "1panel",
"vendor": "fit2cloud",
"versions": [
{
"lessThan": "1.10.1-lts",
"status": "affected",
"version": "0",
"versionType": "custom"
}
]
}
],
"source": "134c704f-9b21-4f2e-91b3-4a467353bcc0"
}
],
"configurations": [
{
"nodes": [
{
"cpeMatch": [
{
"criteria": "cpe:2.3:a:fit2cloud:1panel:*:*:*:*:*:*:*:*",
"matchCriteriaId": "7A1FF200-6BEE-4291-B01A-5052832CB11F",
"versionEndExcluding": "1.10.1-lts",
"vulnerable": true
}
],
"negate": false,
"operator": "OR"
}
]
}
],
"cveTags": [],
"descriptions": [
{
"lang": "en",
"value": "1Panel is an open source Linux server operation and maintenance management panel. Prior to version 1.10.1-lts, users can use Burp to obtain unauthorized access to the console page. The vulnerability has been fixed in v1.10.1-lts. There are no known workarounds."
},
{
"lang": "es",
"value": "1Panel es un panel de gesti\u00f3n de operaci\u00f3n y mantenimiento de servidores Linux de c\u00f3digo abierto. Antes de la versi\u00f3n 1.10.1-lts, los usuarios pod\u00edan usar Burp para obtener acceso no autorizado a la p\u00e1gina de la consola. La vulnerabilidad se ha solucionado en v1.10.1-lts. No se conocen workarounds."
}
],
"id": "CVE-2024-27288",
"lastModified": "2026-06-17T07:19:34.880",
"metrics": {
"cvssMetricV31": [
{
"cvssData": {
"attackComplexity": "LOW",
"attackVector": "NETWORK",
"availabilityImpact": "LOW",
"baseScore": 6.3,
"baseSeverity": "MEDIUM",
"confidentialityImpact": "LOW",
"integrityImpact": "LOW",
"privilegesRequired": "NONE",
"scope": "UNCHANGED",
"userInteraction": "REQUIRED",
"vectorString": "CVSS:3.1/AV:N/AC:L/PR:N/UI:R/S:U/C:L/I:L/A:L",
"version": "3.1"
},
"exploitabilityScore": 2.8,
"impactScore": 3.4,
"source": "security-advisories@github.com",
"type": "Secondary"
},
{
"cvssData": {
"attackComplexity": "HIGH",
"attackVector": "NETWORK",
"availabilityImpact": "NONE",
"baseScore": 3.1,
"baseSeverity": "LOW",
"confidentialityImpact": "LOW",
"integrityImpact": "NONE",
"privilegesRequired": "NONE",
"scope": "UNCHANGED",
"userInteraction": "REQUIRED",
"vectorString": "CVSS:3.1/AV:N/AC:H/PR:N/UI:R/S:U/C:L/I:N/A:N",
"version": "3.1"
},
"exploitabilityScore": 1.6,
"impactScore": 1.4,
"source": "nvd@nist.gov",
"type": "Primary"
}
],
"ssvcV203": [
{
"source": "134c704f-9b21-4f2e-91b3-4a467353bcc0",
"ssvcData": {
"id": "CVE-2024-27288",
"options": [
{
"exploitation": "poc"
},
{
"automatable": "no"
},
{
"technicalImpact": "partial"
}
],
"role": "CISA Coordinator",
"timestamp": "2024-08-27T16:50:21.682289Z",
"version": "2.0.3"
}
}
]
},
"published": "2024-03-06T19:15:07.933",
"references": [
{
"source": "security-advisories@github.com",
"tags": [
"Release Notes"
],
"url": "https://github.com/1Panel-dev/1Panel/releases/tag/v1.10.1-lts"
},
{
"source": "security-advisories@github.com",
"tags": [
"Exploit",
"Vendor Advisory"
],
"url": "https://github.com/1Panel-dev/1Panel/security/advisories/GHSA-26w3-q4j8-4xjp"
},
{
"source": "af854a3a-2127-422b-91ae-364da2661108",
"tags": [
"Release Notes"
],
"url": "https://github.com/1Panel-dev/1Panel/releases/tag/v1.10.1-lts"
},
{
"source": "af854a3a-2127-422b-91ae-364da2661108",
"tags": [
"Exploit",
"Vendor Advisory"
],
"url": "https://github.com/1Panel-dev/1Panel/security/advisories/GHSA-26w3-q4j8-4xjp"
}
],
"sourceIdentifier": "security-advisories@github.com",
"vulnStatus": "Analyzed",
"weaknesses": [
{
"description": [
{
"lang": "en",
"value": "CWE-863"
}
],
"source": "security-advisories@github.com",
"type": "Secondary"
},
{
"description": [
{
"lang": "en",
"value": "CWE-863"
}
],
"source": "nvd@nist.gov",
"type": "Primary"
}
]
}
},
"redhat_vex": {
"current_release_date": "2025-05-28T21:57:04+00:00",
"cve": "CVE-2024-27288",
"id": "CVE-2024-27288",
"initial_release_date": "2024-01-01T00:00:00+00:00",
"product_status:known_not_affected": "1",
"source": "Red Hat CSAF VEX",
"status": "final",
"title": "1Panel open source panel project has an unauthorized vulnerability.",
"url": "https://security.access.redhat.com/data/csaf/v2/vex/2024/cve-2024-27288.json",
"version": "3"
},
"vulnrichment": {
"containers": {
"adp": [
{
"providerMetadata": {
"dateUpdated": "2024-08-02T00:28:00.342Z",
"orgId": "af854a3a-2127-422b-91ae-364da2661108",
"shortName": "CVE"
},
"references": [
{
"name": "https://github.com/1Panel-dev/1Panel/security/advisories/GHSA-26w3-q4j8-4xjp",
"tags": [
"x_refsource_CONFIRM",
"x_transferred"
],
"url": "https://github.com/1Panel-dev/1Panel/security/advisories/GHSA-26w3-q4j8-4xjp"
},
{
"name": "https://github.com/1Panel-dev/1Panel/releases/tag/v1.10.1-lts",
"tags": [
"x_refsource_MISC",
"x_transferred"
],
"url": "https://github.com/1Panel-dev/1Panel/releases/tag/v1.10.1-lts"
}
],
"title": "CVE Program Container"
},
{
"affected": [
{
"cpes": [
"cpe:2.3:a:fit2cloud:1panel:*:*:*:*:*:*:*:*"
],
"defaultStatus": "unknown",
"product": "1panel",
"vendor": "fit2cloud",
"versions": [
{
"lessThan": "1.10.1-lts",
"status": "affected",
"version": "0",
"versionType": "custom"
}
]
}
],
"metrics": [
{
"other": {
"content": {
"id": "CVE-2024-27288",
"options": [
{
"Exploitation": "poc"
},
{
"Automatable": "no"
},
{
"Technical Impact": "partial"
}
],
"role": "CISA Coordinator",
"timestamp": "2024-08-27T16:50:21.682289Z",
"version": "2.0.3"
},
"type": "ssvc"
}
}
],
"providerMetadata": {
"dateUpdated": "2024-08-27T16:52:47.319Z",
"orgId": "134c704f-9b21-4f2e-91b3-4a467353bcc0",
"shortName": "CISA-ADP"
},
"title": "CISA ADP Vulnrichment"
}
],
"cna": {
"affected": [
{
"product": "1Panel",
"vendor": "1Panel-dev",
"versions": [
{
"status": "affected",
"version": "\u003c 1.10.1-lts"
}
]
}
],
"descriptions": [
{
"lang": "en",
"value": "1Panel is an open source Linux server operation and maintenance management panel. Prior to version 1.10.1-lts, users can use Burp to obtain unauthorized access to the console page. The vulnerability has been fixed in v1.10.1-lts. There are no known workarounds."
}
],
"metrics": [
{
"cvssV3_1": {
"attackComplexity": "LOW",
"attackVector": "NETWORK",
"availabilityImpact": "LOW",
"baseScore": 6.3,
"baseSeverity": "MEDIUM",
"confidentialityImpact": "LOW",
"integrityImpact": "LOW",
"privilegesRequired": "NONE",
"scope": "UNCHANGED",
"userInteraction": "REQUIRED",
"vectorString": "CVSS:3.1/AV:N/AC:L/PR:N/UI:R/S:U/C:L/I:L/A:L",
"version": "3.1"
}
}
],
"problemTypes": [
{
"descriptions": [
{
"cweId": "CWE-863",
"description": "CWE-863: Incorrect Authorization",
"lang": "en",
"type": "CWE"
}
]
}
],
"providerMetadata": {
"dateUpdated": "2024-03-06T18:23:50.053Z",
"orgId": "a0819718-46f1-4df5-94e2-005712e83aaa",
"shortName": "GitHub_M"
},
"references": [
{
"name": "https://github.com/1Panel-dev/1Panel/security/advisories/GHSA-26w3-q4j8-4xjp",
"tags": [
"x_refsource_CONFIRM"
],
"url": "https://github.com/1Panel-dev/1Panel/security/advisories/GHSA-26w3-q4j8-4xjp"
},
{
"name": "https://github.com/1Panel-dev/1Panel/releases/tag/v1.10.1-lts",
"tags": [
"x_refsource_MISC"
],
"url": "https://github.com/1Panel-dev/1Panel/releases/tag/v1.10.1-lts"
}
],
"source": {
"advisory": "GHSA-26w3-q4j8-4xjp",
"discovery": "UNKNOWN"
},
"title": "1Panel open source panel project has an unauthorized vulnerability."
}
},
"cveMetadata": {
"assignerOrgId": "a0819718-46f1-4df5-94e2-005712e83aaa",
"assignerShortName": "GitHub_M",
"cveId": "CVE-2024-27288",
"datePublished": "2024-03-06T18:23:50.053Z",
"dateReserved": "2024-02-22T18:08:38.873Z",
"dateUpdated": "2024-08-27T16:52:53.993Z",
"state": "PUBLISHED"
},
"dataType": "CVE_RECORD",
"dataVersion": "5.1"
}
}
}
FKIE_CVE-2024-27288
Vulnerability from fkie_nvd - Published: 2024-03-06 19:15 - Updated: 2026-06-17 07:193.1 (Low) - CVSS:3.1/
{
  "affected": [
    {
      "affectedData": [
        {
          "product": "1Panel",
          "vendor": "1Panel-dev",
          "versions": [
            {
              "status": "affected",
              "version": "\u003c 1.10.1-lts"
            }
          ]
        }
      ],
      "source": "security-advisories@github.com"
    },
    {
      "affectedData": [
        {
          "cpes": [
            "cpe:2.3:a:fit2cloud:1panel:*:*:*:*:*:*:*:*"
          ],
          "defaultStatus": "unknown",
          "product": "1panel",
          "vendor": "fit2cloud",
          "versions": [
            {
              "lessThan": "1.10.1-lts",
              "status": "affected",
              "version": "0",
              "versionType": "custom"
            }
          ]
        }
      ],
      "source": "134c704f-9b21-4f2e-91b3-4a467353bcc0"
    }
  ],
  "configurations": [
    {
      "nodes": [
        {
          "cpeMatch": [
            {
              "criteria": "cpe:2.3:a:fit2cloud:1panel:*:*:*:*:*:*:*:*",
              "matchCriteriaId": "7A1FF200-6BEE-4291-B01A-5052832CB11F",
              "versionEndExcluding": "1.10.1-lts",
              "vulnerable": true
            }
          ],
          "negate": false,
          "operator": "OR"
        }
      ]
    }
  ],
  "cveTags": [],
  "descriptions": [
    {
      "lang": "en",
      "value": "1Panel is an open source Linux server operation and maintenance management panel. Prior to version 1.10.1-lts, users can use Burp to obtain unauthorized access to the console page. The vulnerability has been fixed in v1.10.1-lts. There are no known workarounds."
    },
    {
      "lang": "es",
      "value": "1Panel es un panel de gesti\u00f3n de operaci\u00f3n y mantenimiento de servidores Linux de c\u00f3digo abierto. Antes de la versi\u00f3n 1.10.1-lts, los usuarios pod\u00edan usar Burp para obtener acceso no autorizado a la p\u00e1gina de la consola. La vulnerabilidad se ha solucionado en v1.10.1-lts. No se conocen workarounds."
    }
  ],
  "id": "CVE-2024-27288",
  "lastModified": "2026-06-17T07:19:34.880",
  "metrics": {
    "cvssMetricV31": [
      {
        "cvssData": {
          "attackComplexity": "LOW",
          "attackVector": "NETWORK",
          "availabilityImpact": "LOW",
          "baseScore": 6.3,
          "baseSeverity": "MEDIUM",
          "confidentialityImpact": "LOW",
          "integrityImpact": "LOW",
          "privilegesRequired": "NONE",
          "scope": "UNCHANGED",
          "userInteraction": "REQUIRED",
          "vectorString": "CVSS:3.1/AV:N/AC:L/PR:N/UI:R/S:U/C:L/I:L/A:L",
          "version": "3.1"
        },
        "exploitabilityScore": 2.8,
        "impactScore": 3.4,
        "source": "security-advisories@github.com",
        "type": "Secondary"
      },
      {
        "cvssData": {
          "attackComplexity": "HIGH",
          "attackVector": "NETWORK",
          "availabilityImpact": "NONE",
          "baseScore": 3.1,
          "baseSeverity": "LOW",
          "confidentialityImpact": "LOW",
          "integrityImpact": "NONE",
          "privilegesRequired": "NONE",
          "scope": "UNCHANGED",
          "userInteraction": "REQUIRED",
          "vectorString": "CVSS:3.1/AV:N/AC:H/PR:N/UI:R/S:U/C:L/I:N/A:N",
          "version": "3.1"
        },
        "exploitabilityScore": 1.6,
        "impactScore": 1.4,
        "source": "nvd@nist.gov",
        "type": "Primary"
      }
    ],
    "ssvcV203": [
      {
        "source": "134c704f-9b21-4f2e-91b3-4a467353bcc0",
        "ssvcData": {
          "id": "CVE-2024-27288",
          "options": [
            {
              "exploitation": "poc"
            },
            {
              "automatable": "no"
            },
            {
              "technicalImpact": "partial"
            }
          ],
          "role": "CISA Coordinator",
          "timestamp": "2024-08-27T16:50:21.682289Z",
          "version": "2.0.3"
        }
      }
    ]
  },
  "published": "2024-03-06T19:15:07.933",
  "references": [
    {
      "source": "security-advisories@github.com",
      "tags": [
        "Release Notes"
      ],
      "url": "https://github.com/1Panel-dev/1Panel/releases/tag/v1.10.1-lts"
    },
    {
      "source": "security-advisories@github.com",
      "tags": [
        "Exploit",
        "Vendor Advisory"
      ],
      "url": "https://github.com/1Panel-dev/1Panel/security/advisories/GHSA-26w3-q4j8-4xjp"
    },
    {
      "source": "af854a3a-2127-422b-91ae-364da2661108",
      "tags": [
        "Release Notes"
      ],
      "url": "https://github.com/1Panel-dev/1Panel/releases/tag/v1.10.1-lts"
    },
    {
      "source": "af854a3a-2127-422b-91ae-364da2661108",
      "tags": [
        "Exploit",
        "Vendor Advisory"
      ],
      "url": "https://github.com/1Panel-dev/1Panel/security/advisories/GHSA-26w3-q4j8-4xjp"
    }
  ],
  "sourceIdentifier": "security-advisories@github.com",
  "vulnStatus": "Analyzed",
  "weaknesses": [
    {
      "description": [
        {
          "lang": "en",
          "value": "CWE-863"
        }
      ],
      "source": "security-advisories@github.com",
      "type": "Secondary"
    },
    {
      "description": [
        {
          "lang": "en",
          "value": "CWE-863"
        }
      ],
      "source": "nvd@nist.gov",
      "type": "Primary"
    }
  ]
}
GHSA-26W3-Q4J8-4XJP
Vulnerability from github – Published: 2024-03-06 15:29 – Updated: 2025-02-11 19:03Impact
The steps are as follows:
-
Access https://IP:PORT/ in the browser, which prompts the user to access with a secure entry point.
-
Use Burp to intercept:
When opening the browser and entering the URL (allowing the first intercepted packet through Burp), the following is displayed:
It is found that in this situation, we can access the console page (although no data is returned and no modification operations can be performed)."
Affected versions: <= 1.10.0-lts
Patches
The vulnerability has been fixed in v1.10.1-lts.
Workarounds
It is recommended to upgrade the version to 1.10.1-lts.
References
If you have any questions or comments about this advisory:
Open an issue in https://github.com/1Panel-dev/1Panel Email us at wanghe@fit2cloud.com
{
"affected": [
{
"database_specific": {
"last_known_affected_version_range": "\u003c= 1.10.0-lts"
},
"package": {
"ecosystem": "Go",
"name": "github.com/1Panel-dev/1Panel"
},
"ranges": [
{
"events": [
{
"introduced": "0"
},
{
"fixed": "1.10.1-lts"
}
],
"type": "ECOSYSTEM"
}
]
}
],
"aliases": [
"CVE-2024-27288"
],
"database_specific": {
"cwe_ids": [
"CWE-863"
],
"github_reviewed": true,
"github_reviewed_at": "2024-03-06T15:29:11Z",
"nvd_published_at": "2024-03-06T19:15:07Z",
"severity": "MODERATE"
},
"details": "### Impact\n\nThe steps are as follows:\n\n1. Access https://IP:PORT/ in the browser, which prompts the user to access with a secure entry point.\n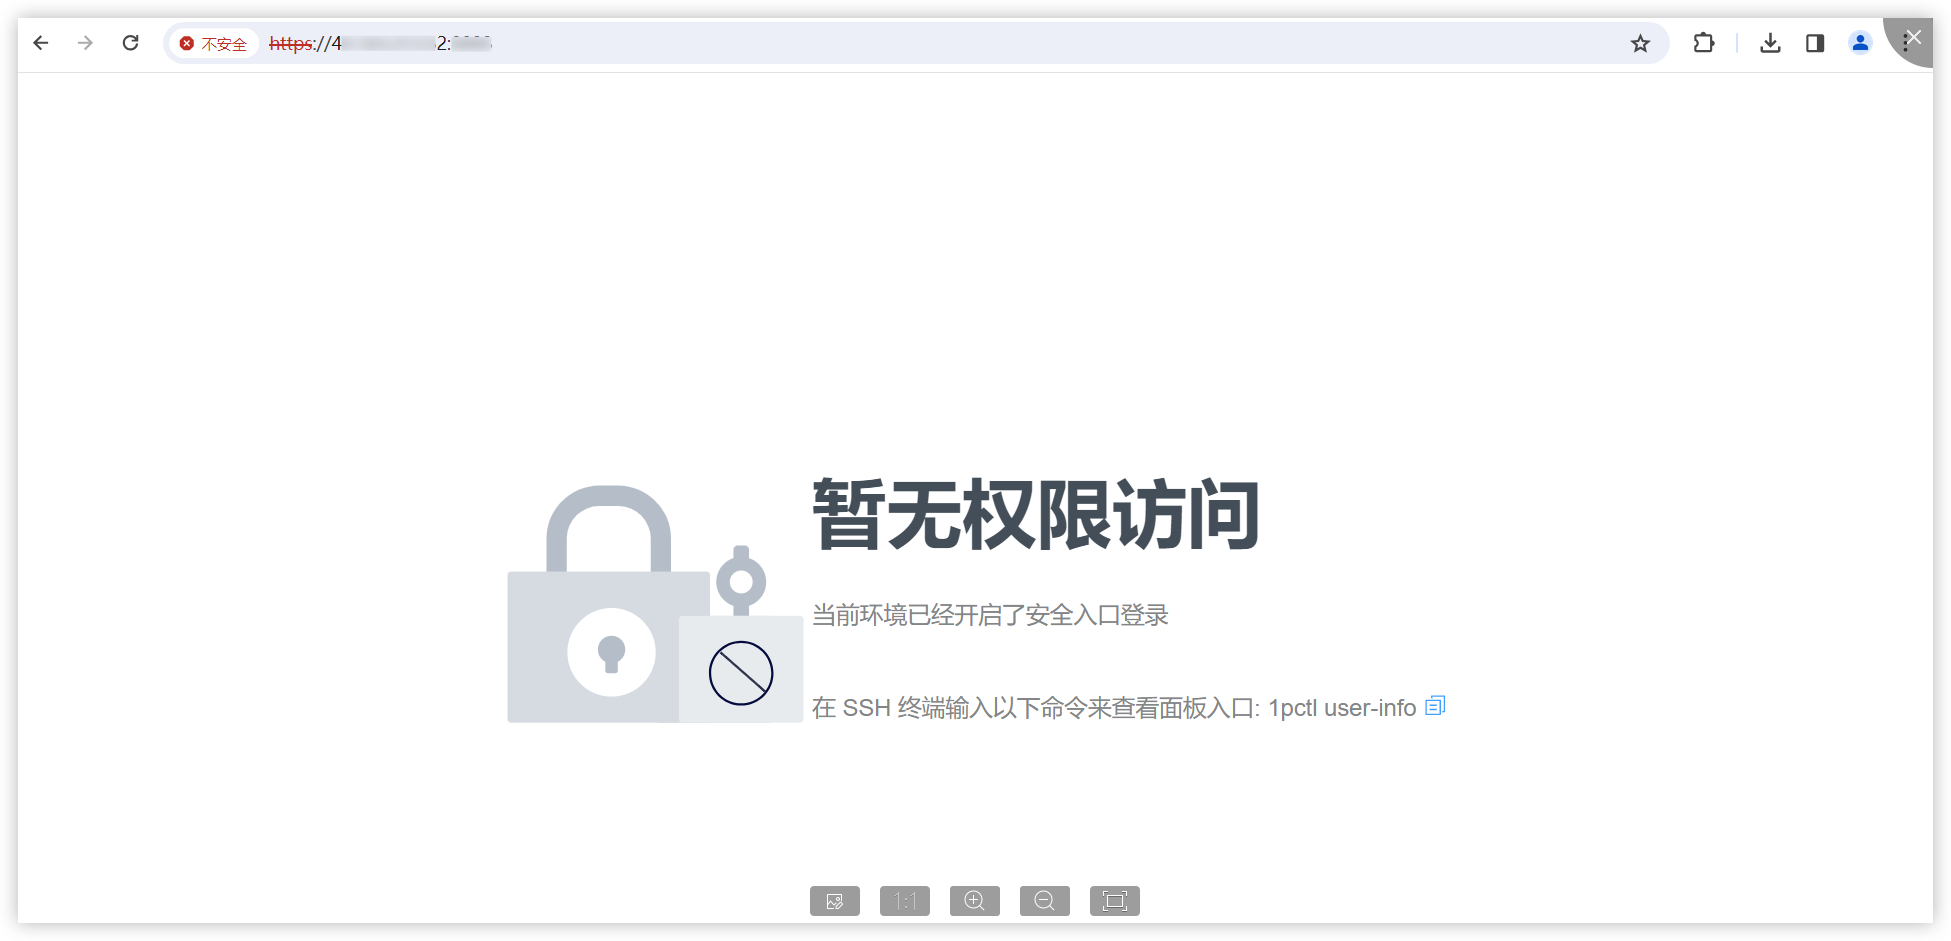\n\n2. Use Burp to intercept:\n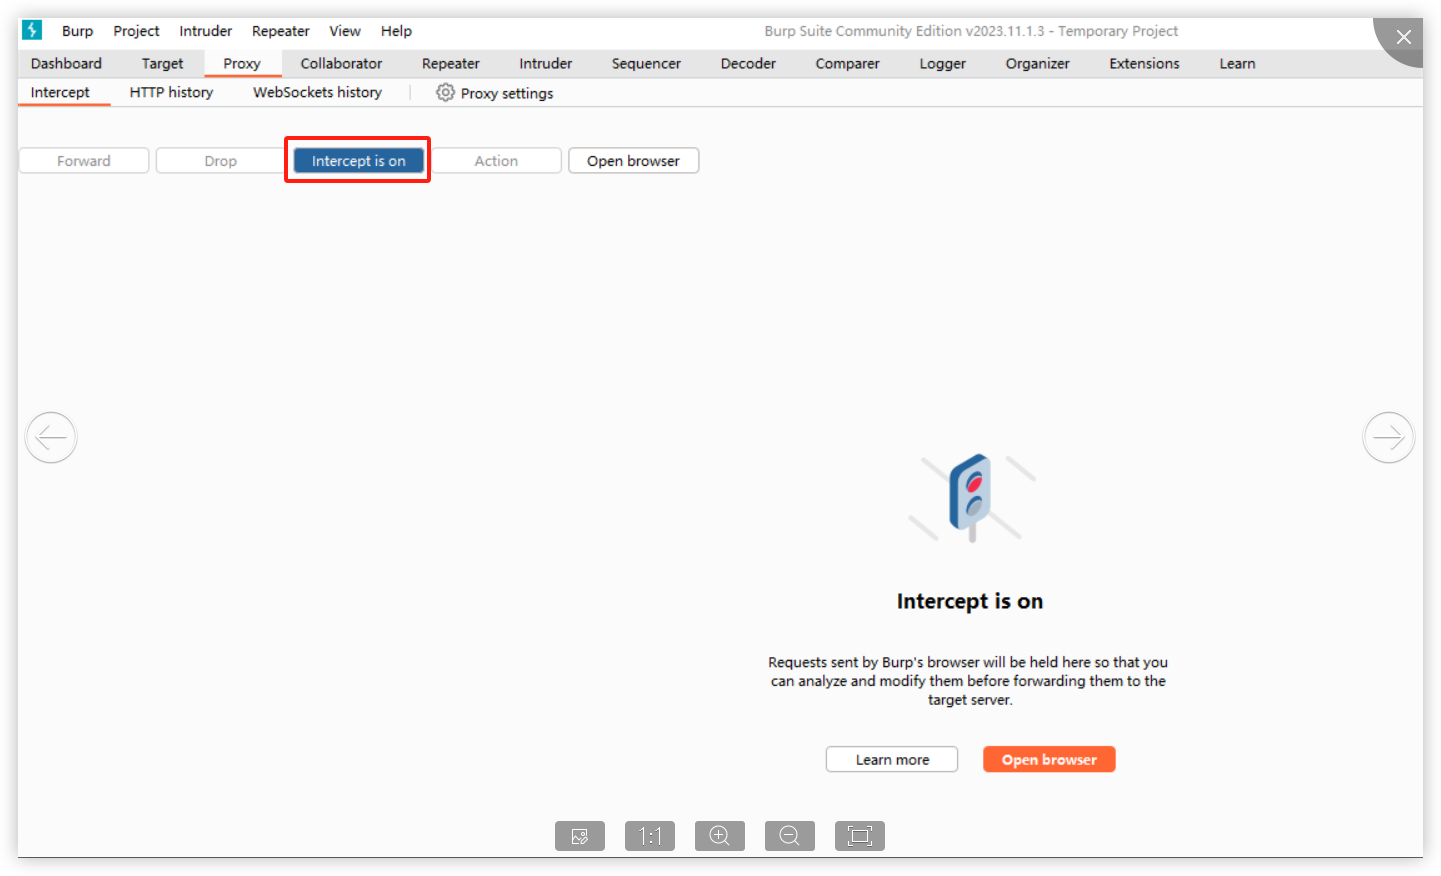\n\nWhen opening the browser and entering the URL (allowing the first intercepted packet through Burp), the following is displayed:\n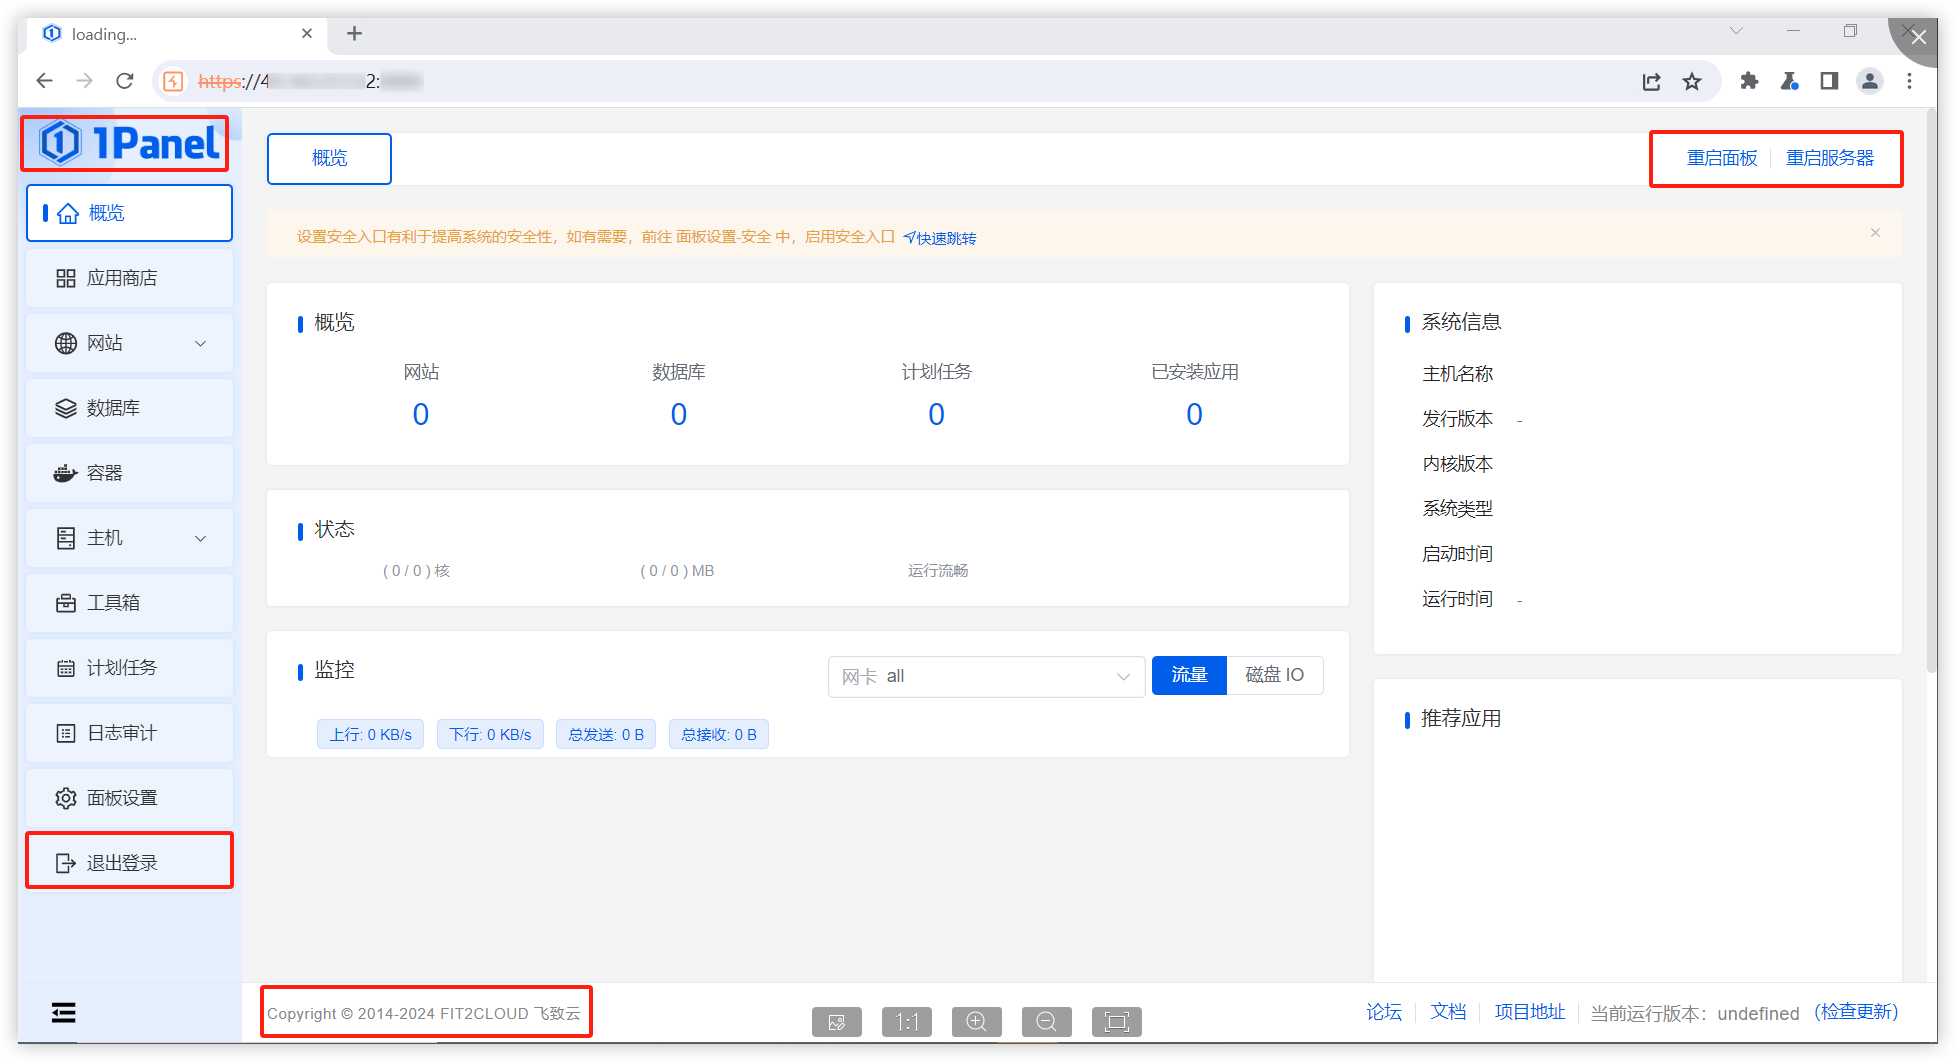\n\nIt is found that in this situation, we can access the console page (although no data is returned and no modification operations can be performed).\"\n\nAffected versions: \u003c= 1.10.0-lts\n\n### Patches\n\nThe vulnerability has been fixed in v1.10.1-lts.\n\n### Workarounds\n\nIt is recommended to upgrade the version to 1.10.1-lts.\n\n### References\n\nIf you have any questions or comments about this advisory:\n\nOpen an issue in https://github.com/1Panel-dev/1Panel\nEmail us at wanghe@fit2cloud.com",
"id": "GHSA-26w3-q4j8-4xjp",
"modified": "2025-02-11T19:03:36Z",
"published": "2024-03-06T15:29:11Z",
"references": [
{
"type": "WEB",
"url": "https://github.com/1Panel-dev/1Panel/security/advisories/GHSA-26w3-q4j8-4xjp"
},
{
"type": "ADVISORY",
"url": "https://nvd.nist.gov/vuln/detail/CVE-2024-27288"
},
{
"type": "WEB",
"url": "https://github.com/1Panel-dev/1Panel/pull/4014"
},
{
"type": "PACKAGE",
"url": "https://github.com/1Panel-dev/1Panel"
},
{
"type": "WEB",
"url": "https://github.com/1Panel-dev/1Panel/releases/tag/v1.10.1-lts"
}
],
"schema_version": "1.4.0",
"severity": [
{
"score": "CVSS:3.1/AV:N/AC:L/PR:N/UI:R/S:U/C:L/I:L/A:L",
"type": "CVSS_V3"
}
],
"summary": "1Panel open source panel project has an unauthorized vulnerability."
}
GSD-2024-27288
Vulnerability from gsd - Updated: 2024-02-23 06:03{
"gsd": {
"metadata": {
"exploitCode": "unknown",
"remediation": "unknown",
"reportConfidence": "confirmed",
"type": "vulnerability"
},
"osvSchema": {
"aliases": [
"CVE-2024-27288"
],
"details": "1Panel is an open source Linux server operation and maintenance management panel. Prior to version 1.10.1-lts, users can use Burp to obtain unauthorized access to the console page. The vulnerability has been fixed in v1.10.1-lts. There are no known workarounds.",
"id": "GSD-2024-27288",
"modified": "2024-02-23T06:03:43.557634Z",
"schema_version": "1.4.0"
}
},
"namespaces": {
"cve.org": {
"CVE_data_meta": {
"ASSIGNER": "security-advisories@github.com",
"ID": "CVE-2024-27288",
"STATE": "PUBLIC"
},
"affects": {
"vendor": {
"vendor_data": [
{
"product": {
"product_data": [
{
"product_name": "1Panel",
"version": {
"version_data": [
{
"version_affected": "=",
"version_value": "\u003c 1.10.1-lts"
}
]
}
}
]
},
"vendor_name": "1Panel-dev"
}
]
}
},
"data_format": "MITRE",
"data_type": "CVE",
"data_version": "4.0",
"description": {
"description_data": [
{
"lang": "eng",
"value": "1Panel is an open source Linux server operation and maintenance management panel. Prior to version 1.10.1-lts, users can use Burp to obtain unauthorized access to the console page. The vulnerability has been fixed in v1.10.1-lts. There are no known workarounds."
}
]
},
"impact": {
"cvss": [
{
"attackComplexity": "LOW",
"attackVector": "NETWORK",
"availabilityImpact": "LOW",
"baseScore": 6.3,
"baseSeverity": "MEDIUM",
"confidentialityImpact": "LOW",
"integrityImpact": "LOW",
"privilegesRequired": "NONE",
"scope": "UNCHANGED",
"userInteraction": "REQUIRED",
"vectorString": "CVSS:3.1/AV:N/AC:L/PR:N/UI:R/S:U/C:L/I:L/A:L",
"version": "3.1"
}
]
},
"problemtype": {
"problemtype_data": [
{
"description": [
{
"cweId": "CWE-863",
"lang": "eng",
"value": "CWE-863: Incorrect Authorization"
}
]
}
]
},
"references": {
"reference_data": [
{
"name": "https://github.com/1Panel-dev/1Panel/security/advisories/GHSA-26w3-q4j8-4xjp",
"refsource": "MISC",
"url": "https://github.com/1Panel-dev/1Panel/security/advisories/GHSA-26w3-q4j8-4xjp"
},
{
"name": "https://github.com/1Panel-dev/1Panel/releases/tag/v1.10.1-lts",
"refsource": "MISC",
"url": "https://github.com/1Panel-dev/1Panel/releases/tag/v1.10.1-lts"
}
]
},
"source": {
"advisory": "GHSA-26w3-q4j8-4xjp",
"discovery": "UNKNOWN"
}
},
"nvd.nist.gov": {
"cve": {
"descriptions": [
{
"lang": "en",
"value": "1Panel is an open source Linux server operation and maintenance management panel. Prior to version 1.10.1-lts, users can use Burp to obtain unauthorized access to the console page. The vulnerability has been fixed in v1.10.1-lts. There are no known workarounds."
}
],
"id": "CVE-2024-27288",
"lastModified": "2024-03-06T21:42:48.053",
"metrics": {
"cvssMetricV31": [
{
"cvssData": {
"attackComplexity": "LOW",
"attackVector": "NETWORK",
"availabilityImpact": "LOW",
"baseScore": 6.3,
"baseSeverity": "MEDIUM",
"confidentialityImpact": "LOW",
"integrityImpact": "LOW",
"privilegesRequired": "NONE",
"scope": "UNCHANGED",
"userInteraction": "REQUIRED",
"vectorString": "CVSS:3.1/AV:N/AC:L/PR:N/UI:R/S:U/C:L/I:L/A:L",
"version": "3.1"
},
"exploitabilityScore": 2.8,
"impactScore": 3.4,
"source": "security-advisories@github.com",
"type": "Secondary"
}
]
},
"published": "2024-03-06T19:15:07.933",
"references": [
{
"source": "security-advisories@github.com",
"url": "https://github.com/1Panel-dev/1Panel/releases/tag/v1.10.1-lts"
},
{
"source": "security-advisories@github.com",
"url": "https://github.com/1Panel-dev/1Panel/security/advisories/GHSA-26w3-q4j8-4xjp"
}
],
"sourceIdentifier": "security-advisories@github.com",
"vulnStatus": "Awaiting Analysis",
"weaknesses": [
{
"description": [
{
"lang": "en",
"value": "CWE-863"
}
],
"source": "security-advisories@github.com",
"type": "Secondary"
}
]
}
}
}
}
Sightings
| Author | Source | Type | Date | Other |
|---|
Nomenclature
- Seen: The vulnerability was mentioned, discussed, or observed by the user.
- Confirmed: The vulnerability has been validated from an analyst's perspective.
- Published Proof of Concept: A public proof of concept is available for this vulnerability.
- Exploited: The vulnerability was observed as exploited by the user who reported the sighting.
- Patched: The vulnerability was observed as successfully patched by the user who reported the sighting.
- Not exploited: The vulnerability was not observed as exploited by the user who reported the sighting.
- Not confirmed: The user expressed doubt about the validity of the vulnerability.
- Not patched: The vulnerability was not observed as successfully patched by the user who reported the sighting.
The approach is described in our paper Mapping CVEs to MITRE ATT&CK Techniques: A Curated Gold-Set Classifier and the Limits of LLM-Assisted Label Expansion.
Browse all ATT&CK techniques and the vulnerabilities related to each.
Related by attack behaviour
Vulnerabilities whose description is nearest to this one in the vector space of the CIRCL/vulnerability-attack-technique-biencoder model. This is a similarity search over the bi-encoder space (plain cosine), not a classification, and it has no measured accuracy.