PYSEC-2026-1817
Vulnerability from pysec - Published: 2026-07-07 11:45 - Updated: 2026-07-07 17:25Summary
Open redirect vulnerability due to incorrect validation of input values when redirecting users after login.
Details
pyload is validating URLs via the get_redirect_url function when redirecting users at login.
The URL entered in the next variable goes through the is_safe_url function, where a lack of validation can redirect the user to an arbitrary domain.
The documentation in the urllib library shows that improper URLs are recognized as relative paths when using the urlparse function. (https://docs.python.org/3/library/urllib.parse.html#urllib.parse.urlparse)
For example, When an unusual URL like https:///example.com is entered, urlparse interprets it as a relative path, but in the actual request it is converted to https://example.com due to url normalization.
PoC
-
In the next variable, insert the URL to which you want to redirect the user.
-
Check that it is possible to bypass url validation and redirect users to an arbitrary url.
Impact
An attacker can use this vulnerability to redirect users to malicious websites, which can be used for phishing and similar attacks.
| Name | purl | pyload-ng | pkg:pypi/pyload-ng |
|---|
{
"affected": [
{
"package": {
"ecosystem": "PyPI",
"name": "pyload-ng",
"purl": "pkg:pypi/pyload-ng"
},
"ranges": [
{
"events": [
{
"introduced": "0"
},
{
"fixed": "0.5.0b3.dev79"
}
],
"type": "ECOSYSTEM"
}
],
"versions": [
"0.5.0a5.dev528",
"0.5.0a5.dev532",
"0.5.0a5.dev535",
"0.5.0a5.dev536",
"0.5.0a5.dev537",
"0.5.0a5.dev539",
"0.5.0a5.dev540",
"0.5.0a5.dev545",
"0.5.0a5.dev562",
"0.5.0a5.dev564",
"0.5.0a5.dev565",
"0.5.0a6.dev570",
"0.5.0a6.dev578",
"0.5.0a6.dev587",
"0.5.0a7.dev596",
"0.5.0a8.dev602",
"0.5.0a9.dev615",
"0.5.0a9.dev629",
"0.5.0a9.dev632",
"0.5.0a9.dev641",
"0.5.0a9.dev643",
"0.5.0a9.dev655",
"0.5.0a9.dev806",
"0.5.0b1.dev1",
"0.5.0b1.dev2",
"0.5.0b1.dev3",
"0.5.0b1.dev4",
"0.5.0b1.dev5",
"0.5.0b2.dev10",
"0.5.0b2.dev11",
"0.5.0b2.dev12",
"0.5.0b2.dev9",
"0.5.0b3.dev13",
"0.5.0b3.dev14",
"0.5.0b3.dev17",
"0.5.0b3.dev18",
"0.5.0b3.dev19",
"0.5.0b3.dev20",
"0.5.0b3.dev21",
"0.5.0b3.dev22",
"0.5.0b3.dev24",
"0.5.0b3.dev26",
"0.5.0b3.dev27",
"0.5.0b3.dev28",
"0.5.0b3.dev29",
"0.5.0b3.dev30",
"0.5.0b3.dev31",
"0.5.0b3.dev32",
"0.5.0b3.dev33",
"0.5.0b3.dev34",
"0.5.0b3.dev35",
"0.5.0b3.dev38",
"0.5.0b3.dev39",
"0.5.0b3.dev40",
"0.5.0b3.dev41",
"0.5.0b3.dev42",
"0.5.0b3.dev43",
"0.5.0b3.dev44",
"0.5.0b3.dev45",
"0.5.0b3.dev46",
"0.5.0b3.dev47",
"0.5.0b3.dev48",
"0.5.0b3.dev49",
"0.5.0b3.dev50",
"0.5.0b3.dev51",
"0.5.0b3.dev52",
"0.5.0b3.dev53",
"0.5.0b3.dev54",
"0.5.0b3.dev57",
"0.5.0b3.dev60",
"0.5.0b3.dev62",
"0.5.0b3.dev64",
"0.5.0b3.dev65",
"0.5.0b3.dev66",
"0.5.0b3.dev67",
"0.5.0b3.dev68",
"0.5.0b3.dev69",
"0.5.0b3.dev70",
"0.5.0b3.dev71",
"0.5.0b3.dev72",
"0.5.0b3.dev73",
"0.5.0b3.dev74",
"0.5.0b3.dev75",
"0.5.0b3.dev76",
"0.5.0b3.dev77",
"0.5.0b3.dev78"
]
}
],
"aliases": [
"CVE-2024-24808",
"GHSA-g3cm-qg2v-2hj5"
],
"details": "### Summary\nOpen redirect vulnerability due to incorrect validation of input values when redirecting users after login.\n\n### Details\npyload is validating URLs via the `get_redirect_url` function when redirecting users at login.\n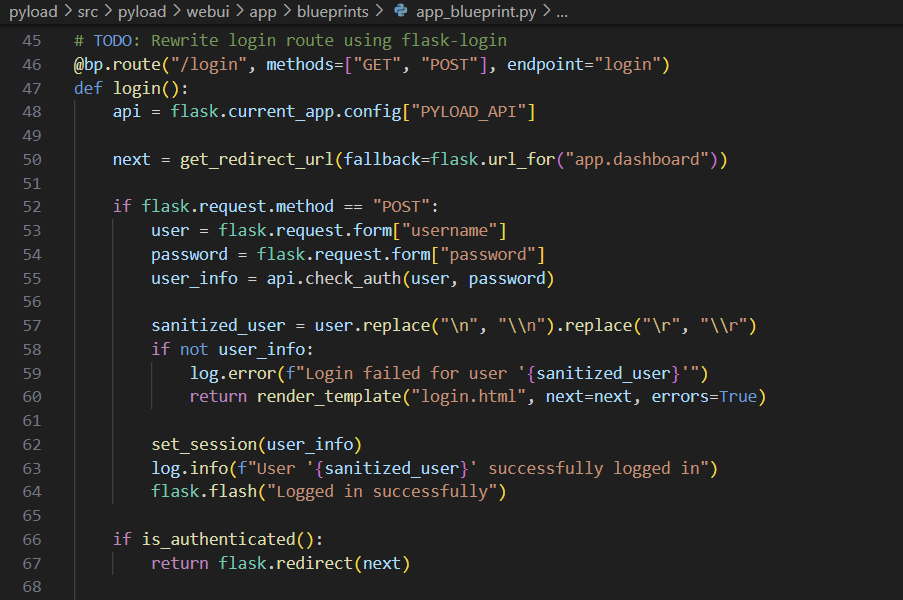\n\n\nThe URL entered in the `next` variable goes through the `is_safe_url` function, where a lack of validation can redirect the user to an arbitrary domain.\n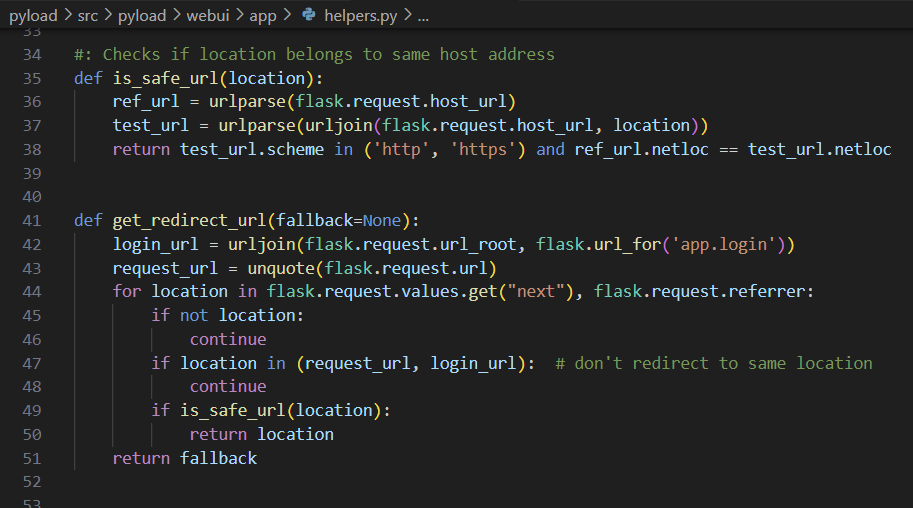\n\n\nThe documentation in the urllib library shows that improper URLs are recognized as relative paths when using the `urlparse` function. (https://docs.python.org/3/library/urllib.parse.html#urllib.parse.urlparse)\n\nFor example, When an unusual URL like `https:///example.com` is entered, `urlparse` interprets it as a relative path, but in the actual request it is converted to `https://example.com` due to url normalization.\n\n### PoC\n1. In the next variable, insert the URL to which you want to redirect the user.\n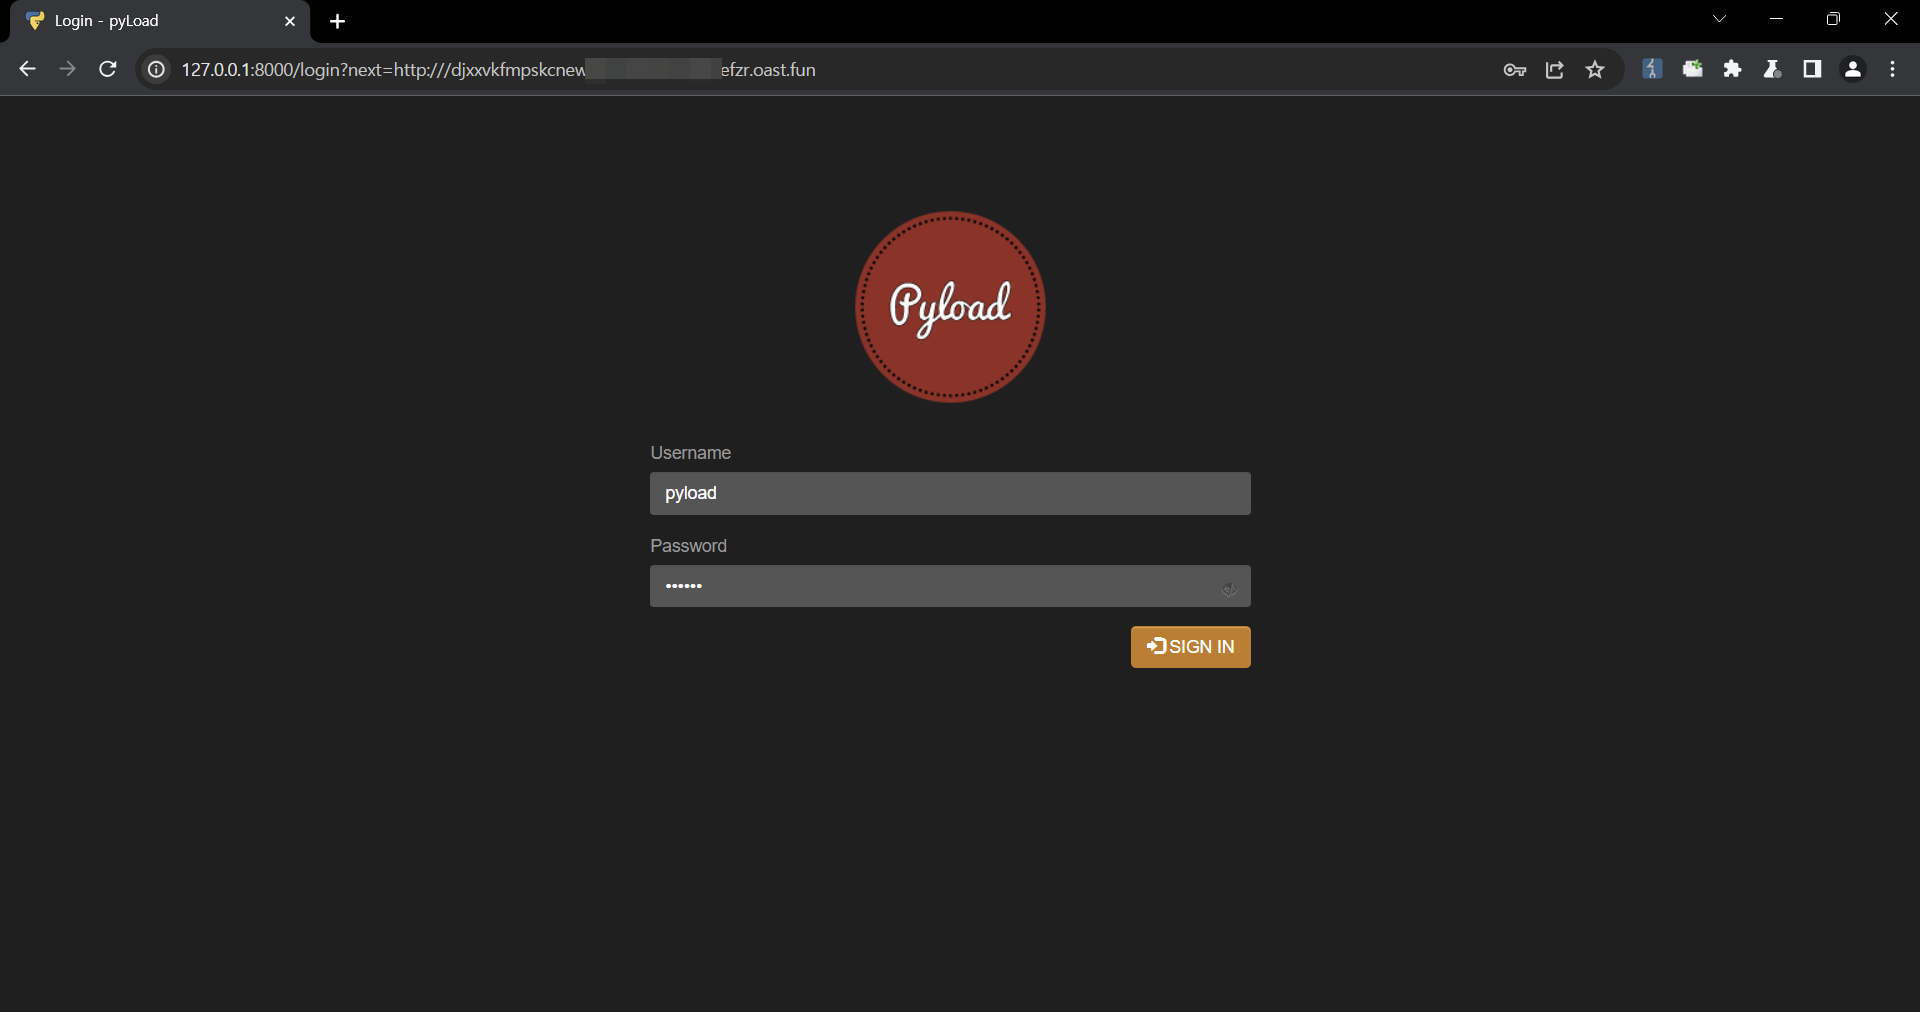\n\n\n\n2. Check that it is possible to bypass url validation and redirect users to an arbitrary url.\n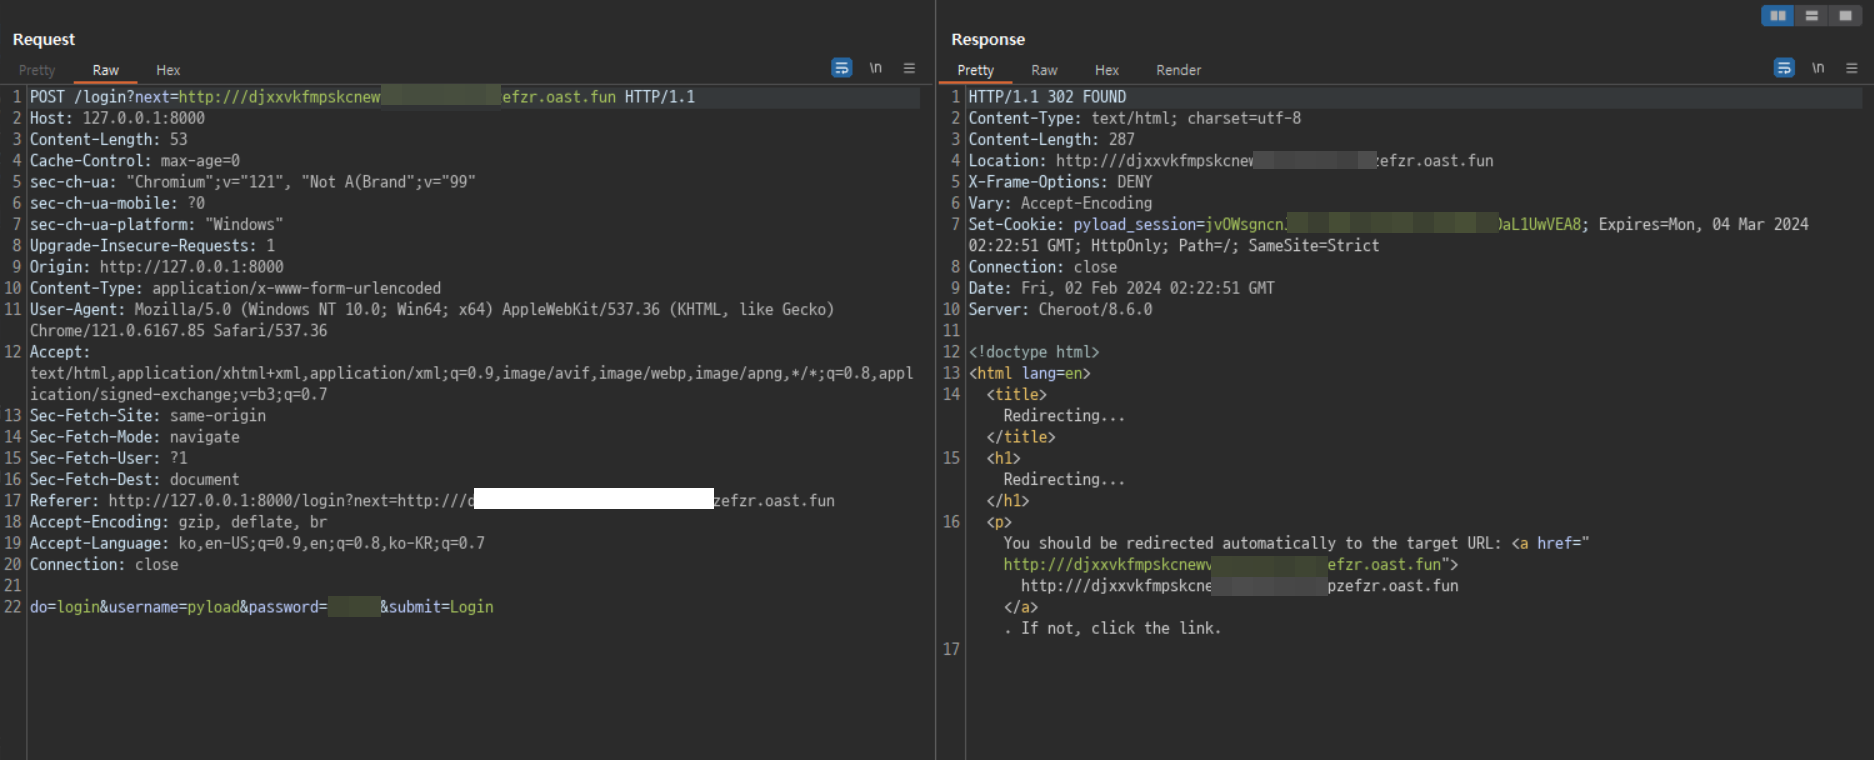\n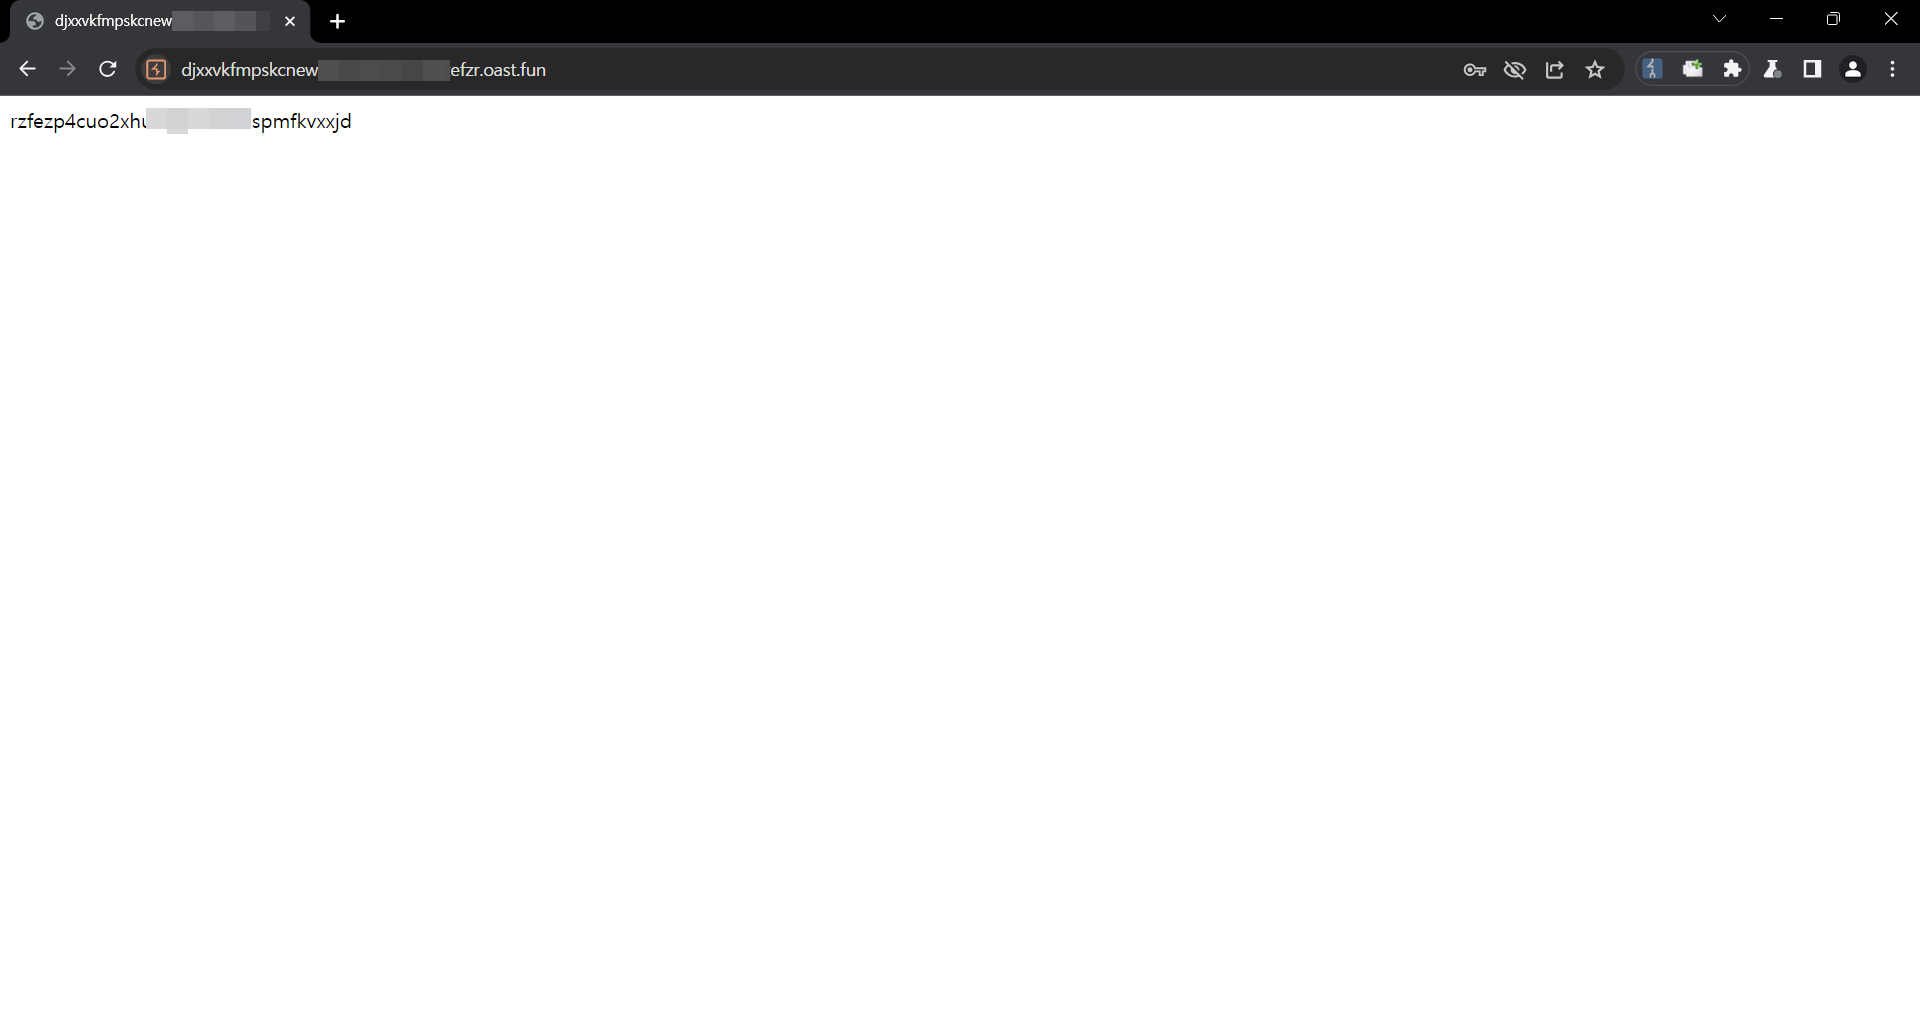\n\n\n\n### Impact\nAn attacker can use this vulnerability to redirect users to malicious websites, which can be used for phishing and similar attacks.\n",
"id": "PYSEC-2026-1817",
"modified": "2026-07-07T17:25:10.866115Z",
"published": "2026-07-07T11:45:32.146458Z",
"references": [
{
"type": "WEB",
"url": "https://github.com/pyload/pyload/security/advisories/GHSA-g3cm-qg2v-2hj5"
},
{
"type": "ADVISORY",
"url": "https://nvd.nist.gov/vuln/detail/CVE-2024-24808"
},
{
"type": "WEB",
"url": "https://github.com/pyload/pyload/commit/fe94451dcc2be90b3889e2fd9d07b483c8a6dccd"
},
{
"type": "PACKAGE",
"url": "https://github.com/pyload/pyload"
},
{
"type": "PACKAGE",
"url": "https://pypi.org/project/pyload-ng"
},
{
"type": "ADVISORY",
"url": "https://github.com/advisories/GHSA-g3cm-qg2v-2hj5"
}
],
"severity": [
{
"score": "CVSS:3.1/AV:N/AC:L/PR:N/UI:R/S:C/C:L/I:L/A:N",
"type": "CVSS_V3"
}
],
"summary": "pyLoad open redirect vulnerability due to improper validation of the is_safe_url function"
}
CVE-2024-24808 (GCVE-0-2024-24808)
Vulnerability from cvelistv5 – Published: 2024-02-06 03:17 – Updated: 2025-05-09 16:31- CWE-601 - URL Redirection to Untrusted Site ('Open Redirect')
| URL | Tags |
|---|---|
| https://github.com/pyload/pyload/security/advisor… | x_refsource_CONFIRM |
| https://github.com/pyload/pyload/commit/fe94451dc… | x_refsource_MISC |
{
  "containers": {
    "adp": [
      {
        "providerMetadata": {
          "dateUpdated": "2024-08-01T23:28:12.795Z",
          "orgId": "af854a3a-2127-422b-91ae-364da2661108",
          "shortName": "CVE"
        },
        "references": [
          {
            "name": "https://github.com/pyload/pyload/security/advisories/GHSA-g3cm-qg2v-2hj5",
            "tags": [
              "x_refsource_CONFIRM",
              "x_transferred"
            ],
            "url": "https://github.com/pyload/pyload/security/advisories/GHSA-g3cm-qg2v-2hj5"
          },
          {
            "name": "https://github.com/pyload/pyload/commit/fe94451dcc2be90b3889e2fd9d07b483c8a6dccd",
            "tags": [
              "x_refsource_MISC",
              "x_transferred"
            ],
            "url": "https://github.com/pyload/pyload/commit/fe94451dcc2be90b3889e2fd9d07b483c8a6dccd"
          }
        ],
        "title": "CVE Program Container"
      },
      {
        "metrics": [
          {
            "other": {
              "content": {
                "id": "CVE-2024-24808",
                "options": [
                  {
                    "Exploitation": "poc"
                  },
                  {
                    "Automatable": "no"
                  },
                  {
                    "Technical Impact": "partial"
                  }
                ],
                "role": "CISA Coordinator",
                "timestamp": "2024-02-06T16:57:09.022075Z",
                "version": "2.0.3"
              },
              "type": "ssvc"
            }
          }
        ],
        "providerMetadata": {
          "dateUpdated": "2025-05-09T16:31:14.196Z",
          "orgId": "134c704f-9b21-4f2e-91b3-4a467353bcc0",
          "shortName": "CISA-ADP"
        },
        "title": "CISA ADP Vulnrichment"
      }
    ],
    "cna": {
      "affected": [
        {
          "product": "pyload",
          "vendor": "pyload",
          "versions": [
            {
              "status": "affected",
              "version": "\u003c= 0.4.20"
            }
          ]
        }
      ],
      "descriptions": [
        {
          "lang": "en",
          "value": "pyLoad is an open-source Download Manager written in pure Python. There is an open redirect vulnerability due to incorrect validation of input values when redirecting users after login. pyLoad is validating URLs via the `get_redirect_url` function when redirecting users at login. This vulnerability has been patched with commit fe94451."
        }
      ],
      "metrics": [
        {
          "cvssV3_1": {
            "attackComplexity": "LOW",
            "attackVector": "NETWORK",
            "availabilityImpact": "NONE",
            "baseScore": 4.7,
            "baseSeverity": "MEDIUM",
            "confidentialityImpact": "LOW",
            "integrityImpact": "NONE",
            "privilegesRequired": "NONE",
            "scope": "CHANGED",
            "userInteraction": "REQUIRED",
            "vectorString": "CVSS:3.1/AV:N/AC:L/PR:N/UI:R/S:C/C:L/I:N/A:N",
            "version": "3.1"
          }
        }
      ],
      "problemTypes": [
        {
          "descriptions": [
            {
              "cweId": "CWE-601",
              "description": "CWE-601: URL Redirection to Untrusted Site (\u0027Open Redirect\u0027)",
              "lang": "en",
              "type": "CWE"
            }
          ]
        }
      ],
      "providerMetadata": {
        "dateUpdated": "2024-02-06T03:17:16.532Z",
        "orgId": "a0819718-46f1-4df5-94e2-005712e83aaa",
        "shortName": "GitHub_M"
      },
      "references": [
        {
          "name": "https://github.com/pyload/pyload/security/advisories/GHSA-g3cm-qg2v-2hj5",
          "tags": [
            "x_refsource_CONFIRM"
          ],
          "url": "https://github.com/pyload/pyload/security/advisories/GHSA-g3cm-qg2v-2hj5"
        },
        {
          "name": "https://github.com/pyload/pyload/commit/fe94451dcc2be90b3889e2fd9d07b483c8a6dccd",
          "tags": [
            "x_refsource_MISC"
          ],
          "url": "https://github.com/pyload/pyload/commit/fe94451dcc2be90b3889e2fd9d07b483c8a6dccd"
        }
      ],
      "source": {
        "advisory": "GHSA-g3cm-qg2v-2hj5",
        "discovery": "UNKNOWN"
      },
      "title": "pyLoad open redirect vulnerability due to improper validation of the is_safe_url function"
    }
  },
  "cveMetadata": {
    "assignerOrgId": "a0819718-46f1-4df5-94e2-005712e83aaa",
    "assignerShortName": "GitHub_M",
    "cveId": "CVE-2024-24808",
    "datePublished": "2024-02-06T03:17:16.532Z",
    "dateReserved": "2024-01-31T16:28:17.941Z",
    "dateUpdated": "2025-05-09T16:31:14.196Z",
    "state": "PUBLISHED"
  },
  "dataType": "CVE_RECORD",
  "dataVersion": "5.1"
}
GHSA-G3CM-QG2V-2HJ5
Vulnerability from github – Published: 2024-02-05 23:23 – Updated: 2024-02-14 14:51Summary
Open redirect vulnerability due to incorrect validation of input values when redirecting users after login.
Details
pyload is validating URLs via the get_redirect_url function when redirecting users at login.
The URL entered in the next variable goes through the is_safe_url function, where a lack of validation can redirect the user to an arbitrary domain.
The documentation in the urllib library shows that improper URLs are recognized as relative paths when using the urlparse function. (https://docs.python.org/3/library/urllib.parse.html#urllib.parse.urlparse)
For example, When an unusual URL like https:///example.com is entered, urlparse interprets it as a relative path, but in the actual request it is converted to https://example.com due to url normalization.
PoC
-
In the next variable, insert the URL to which you want to redirect the user.
-
Check that it is possible to bypass url validation and redirect users to an arbitrary url.
Impact
An attacker can use this vulnerability to redirect users to malicious websites, which can be used for phishing and similar attacks.
{
"affected": [
{
"package": {
"ecosystem": "PyPI",
"name": "pyload-ng"
},
"ranges": [
{
"events": [
{
"introduced": "0"
},
{
"fixed": "0.5.0b3.dev79"
}
],
"type": "ECOSYSTEM"
}
]
}
],
"aliases": [
"CVE-2024-24808"
],
"database_specific": {
"cwe_ids": [
"CWE-601"
],
"github_reviewed": true,
"github_reviewed_at": "2024-02-05T23:23:22Z",
"nvd_published_at": "2024-02-06T04:15:08Z",
"severity": "MODERATE"
},
"details": "### Summary\nOpen redirect vulnerability due to incorrect validation of input values when redirecting users after login.\n\n### Details\npyload is validating URLs via the `get_redirect_url` function when redirecting users at login.\n\n\n\nThe URL entered in the `next` variable goes through the `is_safe_url` function, where a lack of validation can redirect the user to an arbitrary domain.\n\n\n\nThe documentation in the urllib library shows that improper URLs are recognized as relative paths when using the `urlparse` function. (https://docs.python.org/3/library/urllib.parse.html#urllib.parse.urlparse)\n\nFor example, When an unusual URL like `https:///example.com` is entered, `urlparse` interprets it as a relative path, but in the actual request it is converted to `https://example.com` due to url normalization.\n\n### PoC\n1. In the next variable, insert the URL to which you want to redirect the user.\n\n\n\n\n2. Check that it is possible to bypass url validation and redirect users to an arbitrary url.\n\n\n\n\n\n### Impact\nAn attacker can use this vulnerability to redirect users to malicious websites, which can be used for phishing and similar attacks.\n",
"id": "GHSA-g3cm-qg2v-2hj5",
"modified": "2024-02-14T14:51:14Z",
"published": "2024-02-05T23:23:22Z",
"references": [
{
"type": "WEB",
"url": "https://github.com/pyload/pyload/security/advisories/GHSA-g3cm-qg2v-2hj5"
},
{
"type": "ADVISORY",
"url": "https://nvd.nist.gov/vuln/detail/CVE-2024-24808"
},
{
"type": "WEB",
"url": "https://github.com/pyload/pyload/commit/fe94451dcc2be90b3889e2fd9d07b483c8a6dccd"
},
{
"type": "PACKAGE",
"url": "https://github.com/pyload/pyload"
}
],
"schema_version": "1.4.0",
"severity": [
{
"score": "CVSS:3.1/AV:N/AC:L/PR:N/UI:R/S:C/C:L/I:L/A:N",
"type": "CVSS_V3"
}
],
"summary": "pyLoad open redirect vulnerability due to improper validation of the is_safe_url function"
}
Sightings
| Author | Source | Type | Date | Other |
|---|
Nomenclature
- Seen: The vulnerability was mentioned, discussed, or observed by the user.
- Confirmed: The vulnerability has been validated from an analyst's perspective.
- Published Proof of Concept: A public proof of concept is available for this vulnerability.
- Exploited: The vulnerability was observed as exploited by the user who reported the sighting.
- Patched: The vulnerability was observed as successfully patched by the user who reported the sighting.
- Not exploited: The vulnerability was not observed as exploited by the user who reported the sighting.
- Not confirmed: The user expressed doubt about the validity of the vulnerability.
- Not patched: The vulnerability was not observed as successfully patched by the user who reported the sighting.
The approach is described in our paper Mapping CVEs to MITRE ATT&CK Techniques: A Curated Gold-Set Classifier and the Limits of LLM-Assisted Label Expansion.
Browse all ATT&CK techniques and the vulnerabilities related to each.
Related by attack behaviour
Vulnerabilities whose description is nearest to this one in the vector space of the CIRCL/vulnerability-attack-technique-biencoder model. This is a similarity search over the bi-encoder space (plain cosine), not a classification, and it has no measured accuracy.