CWE-80
AllowedImproper Neutralization of Script-Related HTML Tags in a Web Page (Basic XSS)
Abstraction: Variant · Status: Incomplete
The product receives input from an upstream component, but it does not neutralize or incorrectly neutralizes special characters such as "<", ">", and "&" that could be interpreted as web-scripting elements when they are sent to a downstream component that processes web pages.
975 vulnerabilities reference this CWE, most recent first.
GHSA-44CQ-GV9F-H346
Vulnerability from github – Published: 2023-08-04 00:30 – Updated: 2024-01-25 18:30A vulnerability in the web-based management interface of Cisco Small Business SPA500 Series IP Phones could allow an unauthenticated, remote attacker to conduct XSS attacks. This vulnerability is due to insufficient validation of user-supplied input by the web-based management interface of the affected software. An attacker could exploit this vulnerability by persuading a user to click a crafted link. A successful exploit could allow the attacker to execute arbitrary script code in the context of the affected interface or access sensitive, browser-based information.
{
  "affected": [],
  "aliases": [
    "CVE-2023-20181"
  ],
  "database_specific": {
    "cwe_ids": [
      "CWE-79",
      "CWE-80"
    ],
    "github_reviewed": false,
    "github_reviewed_at": null,
    "nvd_published_at": "2023-08-03T22:15:10Z",
    "severity": "MODERATE"
  },
  "details": "A vulnerability in the web-based management interface of Cisco Small Business SPA500 Series IP Phones could allow an unauthenticated, remote attacker to conduct XSS attacks. This vulnerability is due to insufficient validation of user-supplied input by the web-based management interface of the affected software. An attacker could exploit this vulnerability by persuading a user to click a crafted link. A successful exploit could allow the attacker to execute arbitrary script code in the context of the affected interface or access sensitive, browser-based information.",
  "id": "GHSA-44cq-gv9f-h346",
  "modified": "2024-01-25T18:30:37Z",
  "published": "2023-08-04T00:30:15Z",
  "references": [
    {
      "type": "ADVISORY",
      "url": "https://nvd.nist.gov/vuln/detail/CVE-2023-20181"
    },
    {
      "type": "WEB",
      "url": "https://sec.cloudapps.cisco.com/security/center/content/CiscoSecurityAdvisory/cisco-sa-spa-web-multi-7kvPmu2F"
    }
  ],
  "schema_version": "1.4.0",
  "severity": [
    {
      "score": "CVSS:3.1/AV:N/AC:L/PR:N/UI:R/S:C/C:L/I:L/A:N",
      "type": "CVSS_V3"
    }
  ]
}
GHSA-44QP-5PM8-6J8P
Vulnerability from github – Published: 2022-05-24 17:19 – Updated: 2025-10-22 00:31An issue was discovered in Roundcube Webmail before 1.3.12 and 1.4.x before 1.4.5. There is XSS via a malicious XML attachment because text/xml is among the allowed types for a preview.
{
  "affected": [],
  "aliases": [
    "CVE-2020-13965"
  ],
  "database_specific": {
    "cwe_ids": [
      "CWE-79",
      "CWE-80"
    ],
    "github_reviewed": false,
    "github_reviewed_at": null,
    "nvd_published_at": "2020-06-09T03:15:00Z",
    "severity": "MODERATE"
  },
  "details": "An issue was discovered in Roundcube Webmail before 1.3.12 and 1.4.x before 1.4.5. There is XSS via a malicious XML attachment because text/xml is among the allowed types for a preview.",
  "id": "GHSA-44qp-5pm8-6j8p",
  "modified": "2025-10-22T00:31:55Z",
  "published": "2022-05-24T17:19:37Z",
  "references": [
    {
      "type": "ADVISORY",
      "url": "https://nvd.nist.gov/vuln/detail/CVE-2020-13965"
    },
    {
      "type": "WEB",
      "url": "https://github.com/roundcube/roundcubemail/commit/884eb611627ef2bd5a2e20e02009ebb1eceecdc3"
    },
    {
      "type": "WEB",
      "url": "https://github.com/DrunkenShells/Disclosures/tree/master/CVE-2020-13965-Cross%20Site-Scripting%20via%20Malicious%20XML%20Attachment-Roundcube"
    },
    {
      "type": "WEB",
      "url": "https://github.com/roundcube/roundcubemail/compare/1.4.4...1.4.5"
    },
    {
      "type": "WEB",
      "url": "https://github.com/roundcube/roundcubemail/releases/tag/1.3.12"
    },
    {
      "type": "WEB",
      "url": "https://github.com/roundcube/roundcubemail/releases/tag/1.4.5"
    },
    {
      "type": "WEB",
      "url": "https://lists.fedoraproject.org/archives/list/package-announce%40lists.fedoraproject.org/message/DLESQ4LPJGMSWHQ4TBRTVQRDG7IXAZCW"
    },
    {
      "type": "WEB",
      "url": "https://lists.fedoraproject.org/archives/list/package-announce%40lists.fedoraproject.org/message/ODPJXBHZ32QSP4MYT2OBCALYXSUJ47SK"
    },
    {
      "type": "WEB",
      "url": "https://lists.fedoraproject.org/archives/list/package-announce@lists.fedoraproject.org/message/DLESQ4LPJGMSWHQ4TBRTVQRDG7IXAZCW"
    },
    {
      "type": "WEB",
      "url": "https://lists.fedoraproject.org/archives/list/package-announce@lists.fedoraproject.org/message/ODPJXBHZ32QSP4MYT2OBCALYXSUJ47SK"
    },
    {
      "type": "WEB",
      "url": "https://roundcube.net/news/2020/06/02/security-updates-1.4.5-and-1.3.12"
    },
    {
      "type": "WEB",
      "url": "https://www.cisa.gov/known-exploited-vulnerabilities-catalog?field_cve=CVE-2020-13965"
    },
    {
      "type": "WEB",
      "url": "https://www.debian.org/security/2020/dsa-4700"
    }
  ],
  "schema_version": "1.4.0",
  "severity": [
    {
      "score": "CVSS:3.1/AV:N/AC:L/PR:N/UI:R/S:C/C:L/I:L/A:N",
      "type": "CVSS_V3"
    }
  ]
}
GHSA-45QG-252V-3F7P
Vulnerability from github – Published: 2026-07-31 19:15 – Updated: 2026-07-31 19:15A <script> element placed directly inside an <svg> (or MathML) container was not removed by Jodit's clean-html sanitizer.
The deny/allow tag filter compared node.nodeName against an upper-cased tag hash, but foreign (SVG/MathML) elements preserve their original-case node names — an SVG script reports "script", not "SCRIPT" — so the default denyTags list (which includes script) did not match it. The script therefore survived in the editor value and serialized output, where it could execute when the content was loaded back into a page or editor.
Proof of concept
<svg xmlns="http://www.w3.org/2000/svg" width="400" height="400" viewBox="0 0 124 124">
  <rect width="124" height="124" rx="24" fill="#000000"></rect>
  <script type="text/javascript">alert(document.domain);</script>
</svg>
Load the payload into the editor (e.g. via source mode) and the <script> is preserved in editor.value and executes.
Impact
Stored / DOM cross-site scripting. An application that persists editor output and later renders or re-opens it in Jodit can have attacker-supplied script run in a victim's (e.g. an administrator's) authenticated browser context.
Patch
Fixed in 4.13.6: the deny/allow lookup now normalises the tag name to upper case before matching, so a foreign namespace can no longer bypass the filter, while allowTags is still honoured.
Workaround
Upgrade to 4.13.6 or later. Server-side sanitization of stored HTML mitigates in the interim.
Credit
Reported by Roman Kis (@CrownKingClown).
{
  "affected": [
    {
      "package": {
        "ecosystem": "npm",
        "name": "jodit"
      },
      "ranges": [
        {
          "events": [
            {
              "introduced": "0"
            },
            {
              "fixed": "4.13.6"
            }
          ],
          "type": "ECOSYSTEM"
        }
      ]
    }
  ],
  "aliases": [
    "CVE-2026-65841"
  ],
  "database_specific": {
    "cwe_ids": [
      "CWE-80"
    ],
    "github_reviewed": true,
    "github_reviewed_at": "2026-07-31T19:15:57Z",
    "nvd_published_at": null,
    "severity": "MODERATE"
  },
  "details": "A `\u003cscript\u003e` element placed directly inside an `\u003csvg\u003e` (or MathML) container was not removed by Jodit\u0027s clean-html sanitizer.\n\nThe deny/allow tag filter compared `node.nodeName` against an upper-cased tag hash, but foreign (SVG/MathML) elements preserve their original-case node names \u2014 an SVG script reports `\"script\"`, not `\"SCRIPT\"` \u2014 so the default `denyTags` list (which includes `script`) did not match it. The script therefore survived in the editor value and serialized output, where it could execute when the content was loaded back into a page or editor.\n\n### Proof of concept\n\n```html\n\u003csvg xmlns=\"http://www.w3.org/2000/svg\" width=\"400\" height=\"400\" viewBox=\"0 0 124 124\"\u003e\n  \u003crect width=\"124\" height=\"124\" rx=\"24\" fill=\"#000000\"\u003e\u003c/rect\u003e\n  \u003cscript type=\"text/javascript\"\u003ealert(document.domain);\u003c/script\u003e\n\u003c/svg\u003e\n```\n\nLoad the payload into the editor (e.g. via source mode) and the `\u003cscript\u003e` is preserved in `editor.value` and executes.\n\n### Impact\n\nStored / DOM cross-site scripting. An application that persists editor output and later renders or re-opens it in Jodit can have attacker-supplied script run in a victim\u0027s (e.g. an administrator\u0027s) authenticated browser context.\n\n### Patch\n\nFixed in **4.13.6**: the deny/allow lookup now normalises the tag name to upper case before matching, so a foreign namespace can no longer bypass the filter, while `allowTags` is still honoured.\n\n### Workaround\n\nUpgrade to 4.13.6 or later. Server-side sanitization of stored HTML mitigates in the interim.\n\n### Credit\n\nReported by Roman Kis (@CrownKingClown).",
  "id": "GHSA-45qg-252v-3f7p",
  "modified": "2026-07-31T19:15:57Z",
  "published": "2026-07-31T19:15:57Z",
  "references": [
    {
      "type": "WEB",
      "url": "https://github.com/xdan/jodit/security/advisories/GHSA-45qg-252v-3f7p"
    },
    {
      "type": "WEB",
      "url": "https://github.com/xdan/jodit/commit/49a31f451f6b686f5610022a1d4406ee85138dc5"
    },
    {
      "type": "PACKAGE",
      "url": "https://github.com/xdan/jodit"
    },
    {
      "type": "WEB",
      "url": "https://github.com/xdan/jodit/releases/tag/4.13.6"
    }
  ],
  "schema_version": "1.4.0",
  "severity": [
    {
      "score": "CVSS:4.0/AV:N/AC:L/AT:N/PR:N/UI:P/VC:N/VI:N/VA:N/SC:L/SI:L/SA:N",
      "type": "CVSS_V4"
    }
  ],
  "summary": "Jodit has cross-site scripting (XSS) via \u003cscript\u003e nested in SVG that bypasses clean-html sanitization"
}
GHSA-4693-86X5-G35M
Vulnerability from github – Published: 2024-10-29 09:30 – Updated: 2024-10-29 09:30The SEUR Oficial plugin for WordPress is vulnerable to Reflected Cross-Site Scripting via the 'change_service' parameter in all versions up to, and including, 2.2.11 due to insufficient input sanitization and output escaping. This makes it possible for unauthenticated attackers to inject arbitrary web scripts in pages that execute if they can successfully trick a user into performing an action such as clicking on a link.
{
  "affected": [],
  "aliases": [
    "CVE-2024-9438"
  ],
  "database_specific": {
    "cwe_ids": [
      "CWE-80"
    ],
    "github_reviewed": false,
    "github_reviewed_at": null,
    "nvd_published_at": "2024-10-29T09:15:12Z",
    "severity": "MODERATE"
  },
  "details": "The SEUR Oficial plugin for WordPress is vulnerable to Reflected Cross-Site Scripting via the \u0027change_service\u0027 parameter in all versions up to, and including, 2.2.11 due to insufficient input sanitization and output escaping. This makes it possible for unauthenticated attackers to inject arbitrary web scripts in pages that execute if they can successfully trick a user into performing an action such as clicking on a link.",
  "id": "GHSA-4693-86x5-g35m",
  "modified": "2024-10-29T09:30:52Z",
  "published": "2024-10-29T09:30:52Z",
  "references": [
    {
      "type": "ADVISORY",
      "url": "https://nvd.nist.gov/vuln/detail/CVE-2024-9438"
    },
    {
      "type": "WEB",
      "url": "https://plugins.trac.wordpress.org/browser/seur/trunk/core/pages/seur-get-labels.php#L60"
    },
    {
      "type": "WEB",
      "url": "https://plugins.trac.wordpress.org/changeset/3176965/seur/trunk/core/pages/seur-get-labels.php"
    },
    {
      "type": "WEB",
      "url": "https://www.wordfence.com/threat-intel/vulnerabilities/id/88edf229-2be2-49d0-b500-e8ff7708f806?source=cve"
    }
  ],
  "schema_version": "1.4.0",
  "severity": [
    {
      "score": "CVSS:3.1/AV:N/AC:L/PR:N/UI:R/S:C/C:L/I:L/A:N",
      "type": "CVSS_V3"
    }
  ]
}
GHSA-47QP-9GRV-HJC7
Vulnerability from github – Published: 2025-05-15 06:31 – Updated: 2025-05-15 06:31The EG-Series plugin for WordPress is vulnerable to Stored Cross-Site Scripting via the plugin's [series] shortcode in all versions up to, and including, 2.1.1 due to insufficient input sanitization and output escaping on user supplied attributes in the shortcode_title function. This makes it possible for authenticated attackers - with contributor-level access and above, on sites with the Classic Editor plugin activated - to inject arbitrary JavaScript code in the titletag attribute that will execute whenever a user access an injected page.
{
  "affected": [],
  "aliases": [
    "CVE-2025-4126"
  ],
  "database_specific": {
    "cwe_ids": [
      "CWE-80"
    ],
    "github_reviewed": false,
    "github_reviewed_at": null,
    "nvd_published_at": "2025-05-15T04:16:17Z",
    "severity": "MODERATE"
  },
  "details": "The EG-Series plugin for WordPress is vulnerable to Stored Cross-Site Scripting via the plugin\u0027s [series] shortcode in all versions up to, and including, 2.1.1 due to insufficient input sanitization and output escaping on user supplied attributes in the shortcode_title function. This makes it possible for authenticated attackers - with contributor-level access and above, on sites with the Classic Editor plugin activated - to inject arbitrary JavaScript code in the titletag attribute that will execute whenever a user access an injected page.",
  "id": "GHSA-47qp-9grv-hjc7",
  "modified": "2025-05-15T06:31:12Z",
  "published": "2025-05-15T06:31:12Z",
  "references": [
    {
      "type": "ADVISORY",
      "url": "https://nvd.nist.gov/vuln/detail/CVE-2025-4126"
    },
    {
      "type": "WEB",
      "url": "https://plugins.trac.wordpress.org/browser/eg-series/trunk/lib/eg-plugin.inc.php#L546"
    },
    {
      "type": "WEB",
      "url": "https://www.wordfence.com/threat-intel/vulnerabilities/id/ab518a1b-304d-4b93-b807-65ef3941dd47?source=cve"
    }
  ],
  "schema_version": "1.4.0",
  "severity": [
    {
      "score": "CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:C/C:L/I:L/A:N",
      "type": "CVSS_V3"
    }
  ]
}
GHSA-48VW-JPF8-HWQH
Vulnerability from github – Published: 2024-03-25 19:45 – Updated: 2024-03-25 22:31Summary
Due to insufficient validation on the contentLink parameter, it is possible for unauthenticated users to inject HTML code to the page which might affect other users. Also, requires that adding new FAQs is allowed for guests and that the admin doesn't check the content of a newly added FAQ.
PoC
-
Browse to ../phpmyfaq/index.php?action=add&cat=0 , enter
https://test.com?p=<h1>HTML_INJECTION</h1>for the contentLink parameter. -
Verify the HTML injection by viewing the FAQ itself, “All categories” → “CategoryName” → ”QuestionName”.
Impact
Attackers can manipulate the appearance and functionality of web pages by injecting malicious HTML code. This can lead to various undesirable outcomes, such as defacing the website, redirecting users to malicious sites, or altering the content to deceive users. Additionally, unauthenticated HTML injection can compromise user privacy by displaying sensitive information or misleading content. It undermines the integrity of the application and erodes user trust, potentially resulting in loss of reputation and credibility.
{
"affected": [
{
"package": {
"ecosystem": "Packagist",
"name": "phpmyfaq/phpmyfaq"
},
"ranges": [
{
"events": [
{
"introduced": "3.2.5"
},
{
"fixed": "3.2.6"
}
],
"type": "ECOSYSTEM"
}
],
"versions": [
"3.2.5"
]
}
],
"aliases": [
"CVE-2024-28108"
],
"database_specific": {
"cwe_ids": [
"CWE-79",
"CWE-80"
],
"github_reviewed": true,
"github_reviewed_at": "2024-03-25T19:45:23Z",
"nvd_published_at": "2024-03-25T19:15:58Z",
"severity": "MODERATE"
},
"details": "### Summary\nDue to insufficient validation on the `contentLink` parameter, it is possible for unauthenticated users to inject HTML code to the page which might affect other users. _Also, requires that adding new FAQs is allowed for guests and that the admin doesn\u0027t check the content of a newly added FAQ._\n\n### PoC\n1. Browse to ../phpmyfaq/index.php?action=add\u0026cat=0 , enter `https://test.com?p=\u003ch1\u003eHTML_INJECTION\u003c/h1\u003e` for the contentLink parameter.\n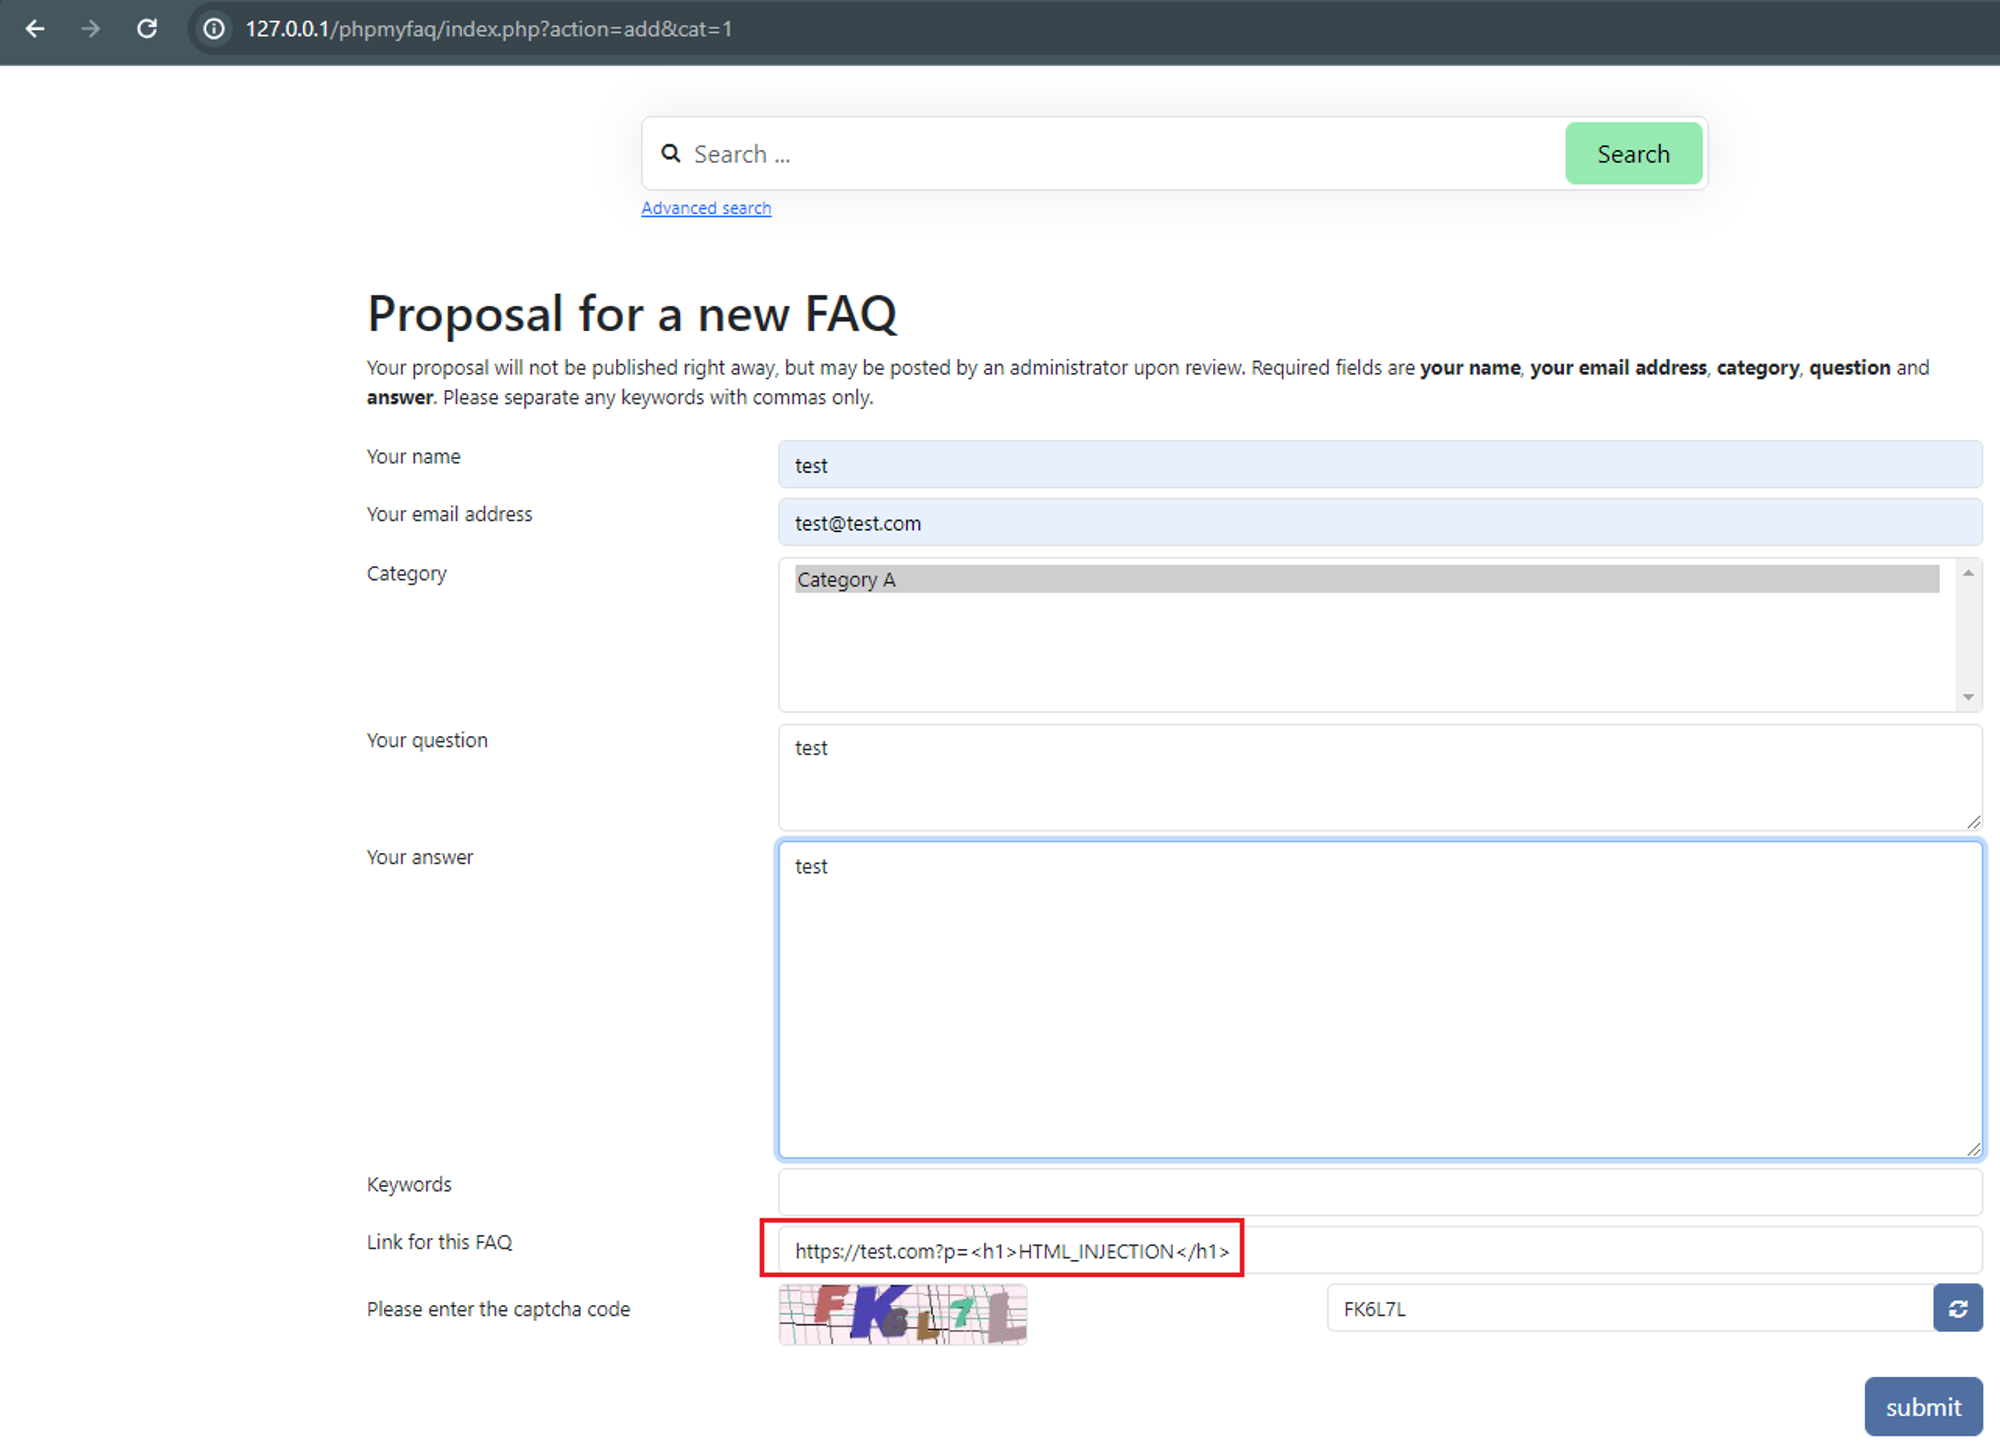\n\n2. Verify the HTML injection by viewing the FAQ itself, \u201cAll categories\u201d \u2192 \u201cCategoryName\u201d \u2192 \u201dQuestionName\u201d.\n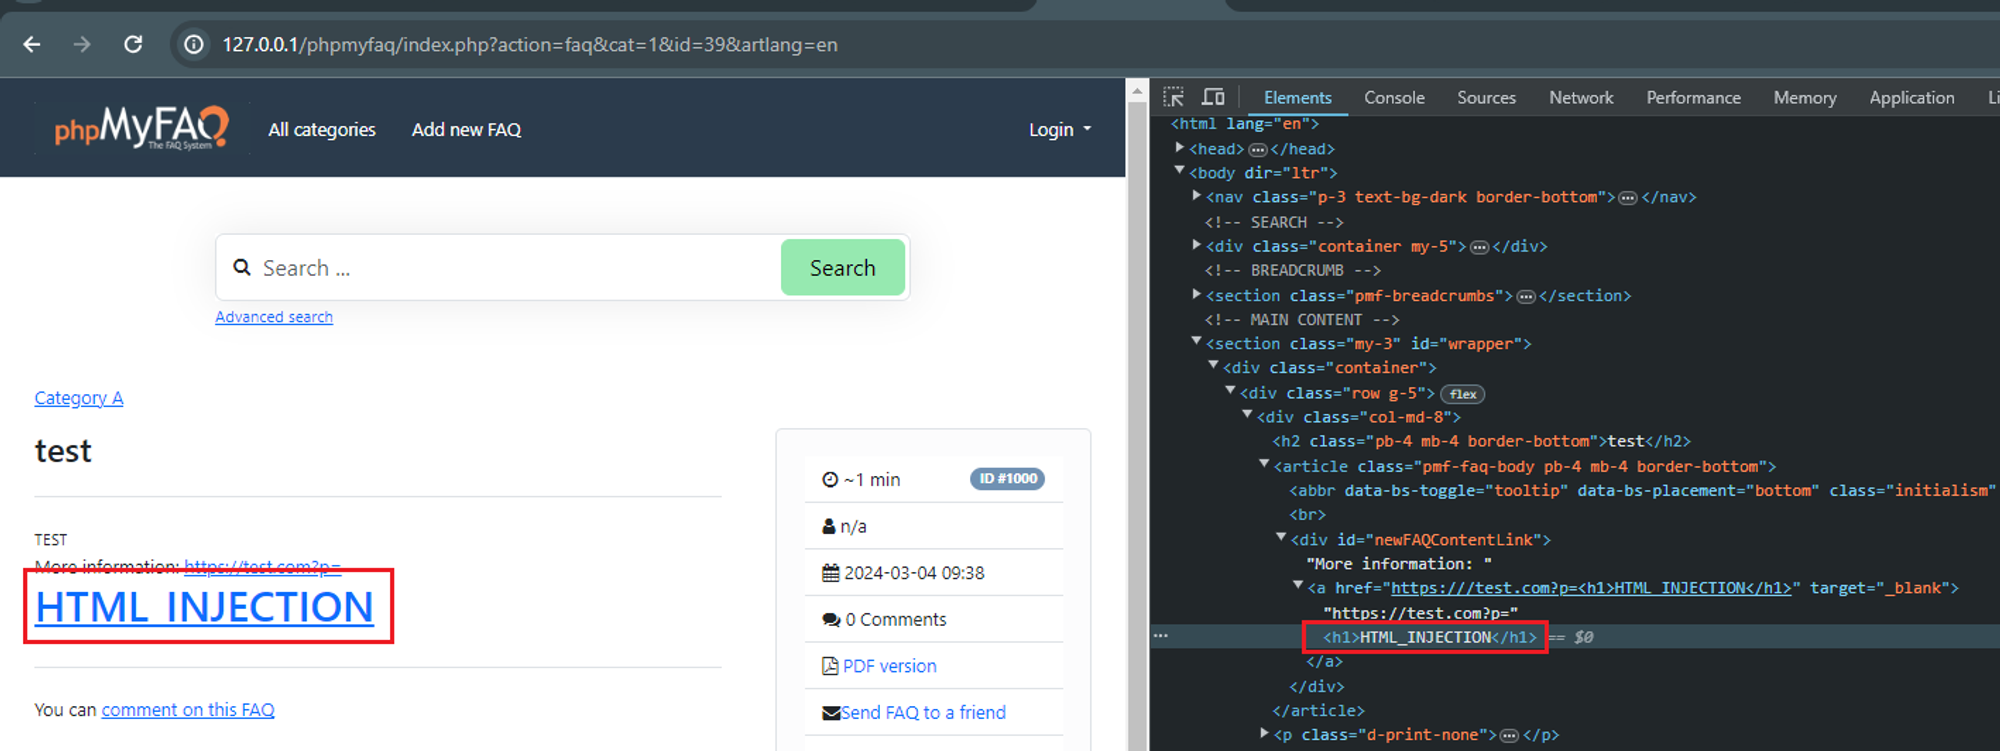\n\n### Impact\nAttackers can manipulate the appearance and functionality of web pages by injecting malicious HTML code. This can lead to various undesirable outcomes, such as defacing the website, redirecting users to malicious sites, or altering the content to deceive users. Additionally, unauthenticated HTML injection can compromise user privacy by displaying sensitive information or misleading content. It undermines the integrity of the application and erodes user trust, potentially resulting in loss of reputation and credibility. ",
"id": "GHSA-48vw-jpf8-hwqh",
"modified": "2024-03-25T22:31:35Z",
"published": "2024-03-25T19:45:23Z",
"references": [
{
"type": "WEB",
"url": "https://github.com/thorsten/phpMyFAQ/security/advisories/GHSA-48vw-jpf8-hwqh"
},
{
"type": "ADVISORY",
"url": "https://nvd.nist.gov/vuln/detail/CVE-2024-28108"
},
{
"type": "WEB",
"url": "https://github.com/thorsten/phpMyFAQ/commit/4fed1d9602f0635260f789fe85995789d94d6634"
},
{
"type": "PACKAGE",
"url": "https://github.com/thorsten/phpMyFAQ"
}
],
"schema_version": "1.4.0",
"severity": [
{
"score": "CVSS:3.1/AV:L/AC:L/PR:N/UI:N/S:U/C:L/I:L/A:N",
"type": "CVSS_V3"
}
],
"summary": "phpMyFAQ Stored HTML Injection at contentLink"
}
GHSA-4FGF-F97H-JG4P
Vulnerability from github – Published: 2023-07-06 19:24 – Updated: 2024-04-04 05:31There is a reflected HTML injection vulnerability in Esri Portal for ArcGIS versions 10.9.1 and below that may allow a remote, unauthenticated attacker to create a crafted link which when clicked could render arbitrary HTML in the victim’s browser.
{
  "affected": [],
  "aliases": [
    "CVE-2022-38210"
  ],
  "database_specific": {
    "cwe_ids": [
      "CWE-79",
      "CWE-80"
    ],
    "github_reviewed": false,
    "github_reviewed_at": null,
    "nvd_published_at": "2022-12-29T20:15:00Z",
    "severity": "MODERATE"
  },
  "details": "There is a reflected HTML injection vulnerability in Esri Portal for ArcGIS versions 10.9.1 and below that may allow a remote, unauthenticated attacker to create a crafted link which when clicked could render arbitrary HTML in the victim\u2019s browser.",
  "id": "GHSA-4fgf-f97h-jg4p",
  "modified": "2024-04-04T05:31:05Z",
  "published": "2023-07-06T19:24:06Z",
  "references": [
    {
      "type": "ADVISORY",
      "url": "https://nvd.nist.gov/vuln/detail/CVE-2022-38210"
    },
    {
      "type": "WEB",
      "url": "https://www.esri.com/arcgis-blog/products/trust-arcgis/administration/portal-for-arcgis-security-2022-update-2-patch-is-now-available"
    }
  ],
  "schema_version": "1.4.0",
  "severity": [
    {
      "score": "CVSS:3.1/AV:N/AC:L/PR:N/UI:R/S:C/C:L/I:L/A:N",
      "type": "CVSS_V3"
    }
  ]
}
GHSA-4GRX-4F48-P5MQ
Vulnerability from github – Published: 2026-04-13 21:30 – Updated: 2026-04-15 18:31A HTML Injection vulnerability exists in the Dashboard module of Vtiger CRM 8.4.0. The application fails to properly neutralize user-supplied input in the tabid parameter of the DashBoardTab view (getTabContents action), allowing an attacker to inject arbitrary HTML content into the dashboard interface. The injected content is rendered in the victim's browser
{
  "affected": [],
  "aliases": [
    "CVE-2026-26460"
  ],
  "database_specific": {
    "cwe_ids": [
      "CWE-80"
    ],
    "github_reviewed": false,
    "github_reviewed_at": null,
    "nvd_published_at": "2026-04-13T21:16:24Z",
    "severity": "MODERATE"
  },
  "details": "A HTML Injection vulnerability exists in the Dashboard module of Vtiger CRM 8.4.0. The application fails to properly neutralize user-supplied input in the tabid parameter of the DashBoardTab view (getTabContents action), allowing an attacker to inject arbitrary HTML content into the dashboard interface. The injected content is rendered in the victim\u0027s browser",
  "id": "GHSA-4grx-4f48-p5mq",
  "modified": "2026-04-15T18:31:52Z",
  "published": "2026-04-13T21:30:44Z",
  "references": [
    {
      "type": "ADVISORY",
      "url": "https://nvd.nist.gov/vuln/detail/CVE-2026-26460"
    },
    {
      "type": "WEB",
      "url": "https://www.simonjuguna.com/cve-2026-26460-html-injection-vulnerability-in-vtiger-open-source-edition-v8-4-0"
    },
    {
      "type": "WEB",
      "url": "https://www.vtiger.com/open-source-crm"
    }
  ],
  "schema_version": "1.4.0",
  "severity": [
    {
      "score": "CVSS:3.1/AV:N/AC:L/PR:N/UI:R/S:C/C:L/I:L/A:N",
      "type": "CVSS_V3"
    }
  ]
}
GHSA-4H7G-5542-V3FC
Vulnerability from github – Published: 2026-07-02 17:51 – Updated: 2026-07-02 17:51Summary
Stored XSS through wikitext can be performed by inserting malicious HTML into the overlays parameter of the display_map parser function when using the leaflet service.
Details
The maps extension doesn't escape overlay names before passing them to leaflet. Leaflet then inserts them as HTML: https://github.com/ProfessionalWiki/Maps/blob/ca5139fabd75f3c34f47ea3fd161306506b053bc/resources/lib/leaflet/leaflet.js#L5243
PoC
Preview the following wikitext, using the default configuration options of the extension:
{{#display_map:0,0|service=leaflet|overlays=OpenTopoMap.<img src=x onerror="alert(1);">}}
Impact
Stored XSS can be performed by any user with the edit permission.
{
  "affected": [
    {
      "package": {
        "ecosystem": "Packagist",
        "name": "mediawiki/maps"
      },
      "ranges": [
        {
          "events": [
            {
              "introduced": "0"
            },
            {
              "fixed": "12.1.3"
            }
          ],
          "type": "ECOSYSTEM"
        }
      ]
    }
  ],
  "aliases": [
    "CVE-2026-52854"
  ],
  "database_specific": {
    "cwe_ids": [
      "CWE-79",
      "CWE-80"
    ],
    "github_reviewed": true,
    "github_reviewed_at": "2026-07-02T17:51:24Z",
    "nvd_published_at": null,
    "severity": "HIGH"
  },
  "details": "### Summary\nStored XSS through wikitext can be performed by inserting malicious HTML into the `overlays` parameter of the `display_map` parser function when using the leaflet service.\n\n### Details\nThe maps extension doesn\u0027t escape overlay names before passing them to leaflet.\nLeaflet then inserts them as HTML: https://github.com/ProfessionalWiki/Maps/blob/ca5139fabd75f3c34f47ea3fd161306506b053bc/resources/lib/leaflet/leaflet.js#L5243\n\n### PoC\nPreview the following wikitext, using the default configuration options of the extension:\n```\n{{#display_map:0,0|service=leaflet|overlays=OpenTopoMap.\u003cimg src=x onerror=\"alert(1);\"\u003e}}\n```\n\n### Impact\nStored XSS can be performed by any user with the `edit` permission.",
  "id": "GHSA-4h7g-5542-v3fc",
  "modified": "2026-07-02T17:51:24Z",
  "published": "2026-07-02T17:51:24Z",
  "references": [
    {
      "type": "WEB",
      "url": "https://github.com/ProfessionalWiki/Maps/security/advisories/GHSA-4h7g-5542-v3fc"
    },
    {
      "type": "PACKAGE",
      "url": "https://github.com/ProfessionalWiki/Maps"
    }
  ],
  "schema_version": "1.4.0",
  "severity": [
    {
      "score": "CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:L/A:L",
      "type": "CVSS_V3"
    }
  ],
  "summary": "mediawiki/maps has stored XSS through the overlays parameter in the display_map parser function"
}
GHSA-4J8P-GHVP-QJV7
Vulnerability from github – Published: 2023-05-31 15:30 – Updated: 2023-05-31 15:30A vulnerability was found in SourceCodester Lost and Found Information System 1.0. It has been classified as problematic. This affects an unknown part of the file admin/?page=user/manage_user of the component Manage User Page. The manipulation of the argument First Name/Middle Name/Last Name leads to basic cross site scripting. It is possible to initiate the attack remotely. The exploit has been disclosed to the public and may be used. The identifier VDB-230361 was assigned to this vulnerability.
{
  "affected": [],
  "aliases": [
    "CVE-2023-3017"
  ],
  "database_specific": {
    "cwe_ids": [
      "CWE-80"
    ],
    "github_reviewed": false,
    "github_reviewed_at": null,
    "nvd_published_at": "2023-05-31T15:15:09Z",
    "severity": "LOW"
  },
  "details": "A vulnerability was found in SourceCodester Lost and Found Information System 1.0. It has been classified as problematic. This affects an unknown part of the file admin/?page=user/manage_user of the component Manage User Page. The manipulation of the argument First Name/Middle Name/Last Name leads to basic cross site scripting. It is possible to initiate the attack remotely. The exploit has been disclosed to the public and may be used. The identifier VDB-230361 was assigned to this vulnerability.",
  "id": "GHSA-4j8p-ghvp-qjv7",
  "modified": "2023-05-31T15:30:20Z",
  "published": "2023-05-31T15:30:20Z",
  "references": [
    {
      "type": "ADVISORY",
      "url": "https://nvd.nist.gov/vuln/detail/CVE-2023-3017"
    },
    {
      "type": "WEB",
      "url": "https://medium.com/@akashpandey380/lost-and-found-information-system-v1-0-html-injection-3596f2b856c0"
    },
    {
      "type": "WEB",
      "url": "https://vuldb.com/?ctiid.230361"
    },
    {
      "type": "WEB",
      "url": "https://vuldb.com/?id.230361"
    }
  ],
  "schema_version": "1.4.0",
  "severity": [
    {
      "score": "CVSS:3.0/AV:N/AC:L/PR:H/UI:R/S:U/C:N/I:L/A:N",
      "type": "CVSS_V3"
    }
  ]
}
Mitigation
Carefully check each input parameter against a rigorous positive specification (allowlist) defining the specific characters and format allowed. All input should be neutralized, not just parameters that the user is supposed to specify, but all data in the request, including hidden fields, cookies, headers, the URL itself, and so forth. A common mistake that leads to continuing XSS vulnerabilities is to validate only fields that are expected to be redisplayed by the site. We often encounter data from the request that is reflected by the application server or the application that the development team did not anticipate. Also, a field that is not currently reflected may be used by a future developer. Therefore, validating ALL parts of the HTTP request is recommended.
Mitigation MIT-30.1
Strategy: Output Encoding
- Use and specify an output encoding that can be handled by the downstream component that is reading the output. Common encodings include ISO-8859-1, UTF-7, and UTF-8. When an encoding is not specified, a downstream component may choose a different encoding, either by assuming a default encoding or automatically inferring which encoding is being used, which can be erroneous. When the encodings are inconsistent, the downstream component might treat some character or byte sequences as special, even if they are not special in the original encoding. Attackers might then be able to exploit this discrepancy and conduct injection attacks; they even might be able to bypass protection mechanisms that assume the original encoding is also being used by the downstream component.
- The problem of inconsistent output encodings often arises in web pages. If an encoding is not specified in an HTTP header, web browsers often guess about which encoding is being used. This can open up the browser to subtle XSS attacks.
Mitigation MIT-43
With Struts, write all data from form beans with the bean's filter attribute set to true.
Mitigation MIT-31
Strategy: Attack Surface Reduction
To help mitigate XSS attacks against the user's session cookie, set the session cookie to be HttpOnly. In browsers that support the HttpOnly feature (such as more recent versions of Internet Explorer and Firefox), this attribute can prevent the user's session cookie from being accessible to malicious client-side scripts that use document.cookie. This is not a complete solution, since HttpOnly is not supported by all browsers. More importantly, XmlHttpRequest and other powerful browser technologies provide read access to HTTP headers, including the Set-Cookie header in which the HttpOnly flag is set.
CAPEC-18: XSS Targeting Non-Script Elements
This attack is a form of Cross-Site Scripting (XSS) where malicious scripts are embedded in elements that are not expected to host scripts such as image tags (<img>), comments in XML documents (< !-CDATA->), etc. These tags may not be subject to the same input validation, output validation, and other content filtering and checking routines, so this can create an opportunity for an adversary to tunnel through the application's elements and launch a XSS attack through other elements. As with all remote attacks, it is important to differentiate the ability to launch an attack (such as probing an internal network for unpatched servers) and the ability of the remote adversary to collect and interpret the output of said attack.
CAPEC-193: PHP Remote File Inclusion
In this pattern the adversary is able to load and execute arbitrary code remotely available from the application. This is usually accomplished through an insecurely configured PHP runtime environment and an improperly sanitized "include" or "require" call, which the user can then control to point to any web-accessible file. This allows adversaries to hijack the targeted application and force it to execute their own instructions.
CAPEC-32: XSS Through HTTP Query Strings
An adversary embeds malicious script code in the parameters of an HTTP query string and convinces a victim to submit the HTTP request that contains the query string to a vulnerable web application. The web application then procedes to use the values parameters without properly validation them first and generates the HTML code that will be executed by the victim's browser.
CAPEC-86: XSS Through HTTP Headers
An adversary exploits web applications that generate web content, such as links in a HTML page, based on unvalidated or improperly validated data submitted by other actors. XSS in HTTP Headers attacks target the HTTP headers which are hidden from most users and may not be validated by web applications.