CWE-613
Allowed-with-ReviewInsufficient Session Expiration
Abstraction: Base · Status: Incomplete
According to WASC, "Insufficient Session Expiration is when a web site permits an attacker to reuse old session credentials or session IDs for authorization."
968 vulnerabilities reference this CWE, most recent first.
GHSA-FH84-5Q42-44P3
Vulnerability from github – Published: 2026-02-05 00:31 – Updated: 2026-02-05 00:31IBM Concert 1.0.0 through 2.1.0 does not invalidate session after logout which could allow an authenticated user to impersonate another user on the system.
{
  "affected": [],
  "aliases": [
    "CVE-2024-43181"
  ],
  "database_specific": {
    "cwe_ids": [
      "CWE-613"
    ],
    "github_reviewed": false,
    "github_reviewed_at": null,
    "nvd_published_at": "2026-02-04T22:15:56Z",
    "severity": "MODERATE"
  },
  "details": "IBM Concert 1.0.0 through 2.1.0 does not invalidate session after logout which could allow an authenticated user to impersonate another user on the system.",
  "id": "GHSA-fh84-5q42-44p3",
  "modified": "2026-02-05T00:31:00Z",
  "published": "2026-02-05T00:31:00Z",
  "references": [
    {
      "type": "ADVISORY",
      "url": "https://nvd.nist.gov/vuln/detail/CVE-2024-43181"
    },
    {
      "type": "WEB",
      "url": "https://www.ibm.com/support/pages/node/7257006"
    }
  ],
  "schema_version": "1.4.0",
  "severity": [
    {
      "score": "CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:L/I:L/A:L",
      "type": "CVSS_V3"
    }
  ]
}
GHSA-FHHF-PQCG-P3JC
Vulnerability from github – Published: 2026-08-04 12:34 – Updated: 2026-08-04 12:34Insufficient session expiration vulnerability in Bilin Software and Informatics Consultancy Inc. HUMANIST Digital Human Resources allows Reusing Session IDs (aka Session Replay).
This issue affects HUMANIST Digital Human Resources: from 26.0 before 26.1.
{
  "affected": [],
  "aliases": [
    "CVE-2026-14465"
  ],
  "database_specific": {
    "cwe_ids": [
      "CWE-613"
    ],
    "github_reviewed": false,
    "github_reviewed_at": null,
    "nvd_published_at": "2026-08-04T10:19:32Z",
    "severity": "MODERATE"
  },
  "details": "Insufficient session expiration vulnerability in Bilin Software and Informatics Consultancy Inc. HUMANIST Digital Human Resources allows Reusing Session IDs (aka Session Replay).\n\nThis issue affects HUMANIST Digital Human Resources: from 26.0 before 26.1.",
  "id": "GHSA-fhhf-pqcg-p3jc",
  "modified": "2026-08-04T12:34:50Z",
  "published": "2026-08-04T12:34:50Z",
  "references": [
    {
      "type": "ADVISORY",
      "url": "https://nvd.nist.gov/vuln/detail/CVE-2026-14465"
    },
    {
      "type": "WEB",
      "url": "https://siberguvenlik.gov.tr/guvenlik-bildirimleri/detay/tr-26-0737"
    }
  ],
  "schema_version": "1.4.0",
  "severity": [
    {
      "score": "CVSS:3.1/AV:N/AC:L/PR:N/UI:R/S:U/C:H/I:N/A:N",
      "type": "CVSS_V3"
    }
  ]
}
GHSA-FJ52-5G4H-GMQ8
Vulnerability from github – Published: 2026-04-14 23:39 – Updated: 2026-04-14 23:39Summary
The pyload application does not properly invalidate or modify sessions upon changes made to a user's permissions.
Details
Whenever an administrator changes the permissions a specific account has, they do not expect that account still being able to access data that their new permissions do not allow. This is not the case for the pyload application, as a user with a valid session can still perform the actions.
PoC
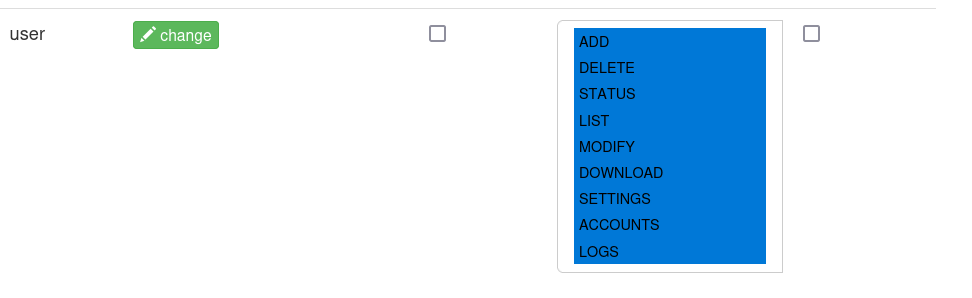
Take a user with all the permissions, as shown below.
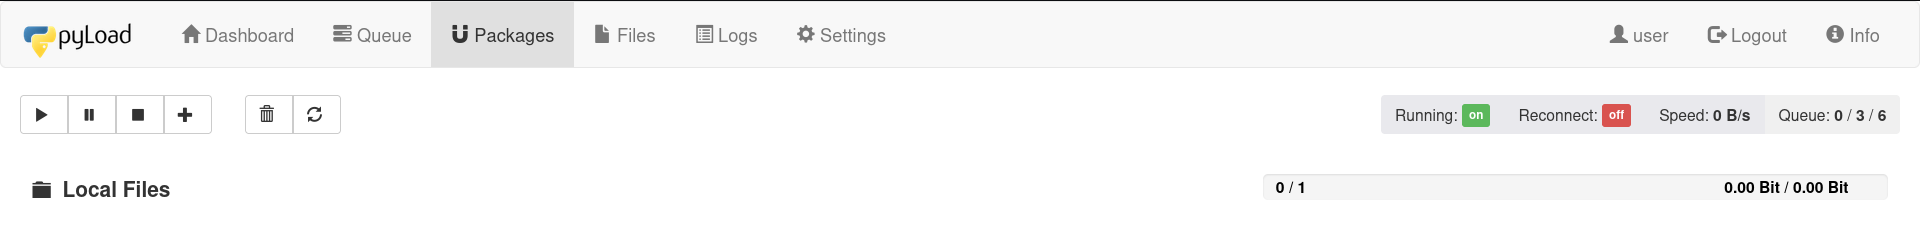
We now log in as this user.
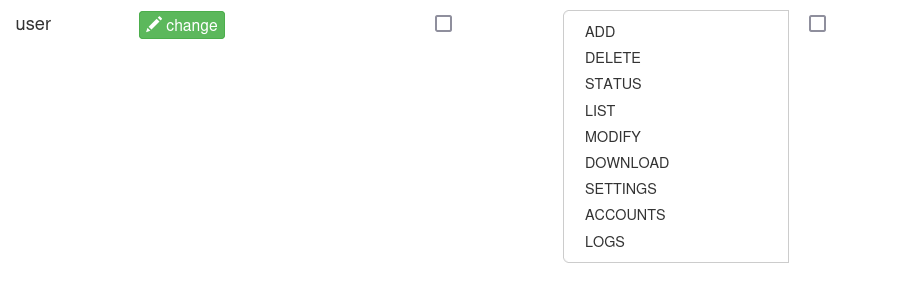
Let us now take away all the permissions.
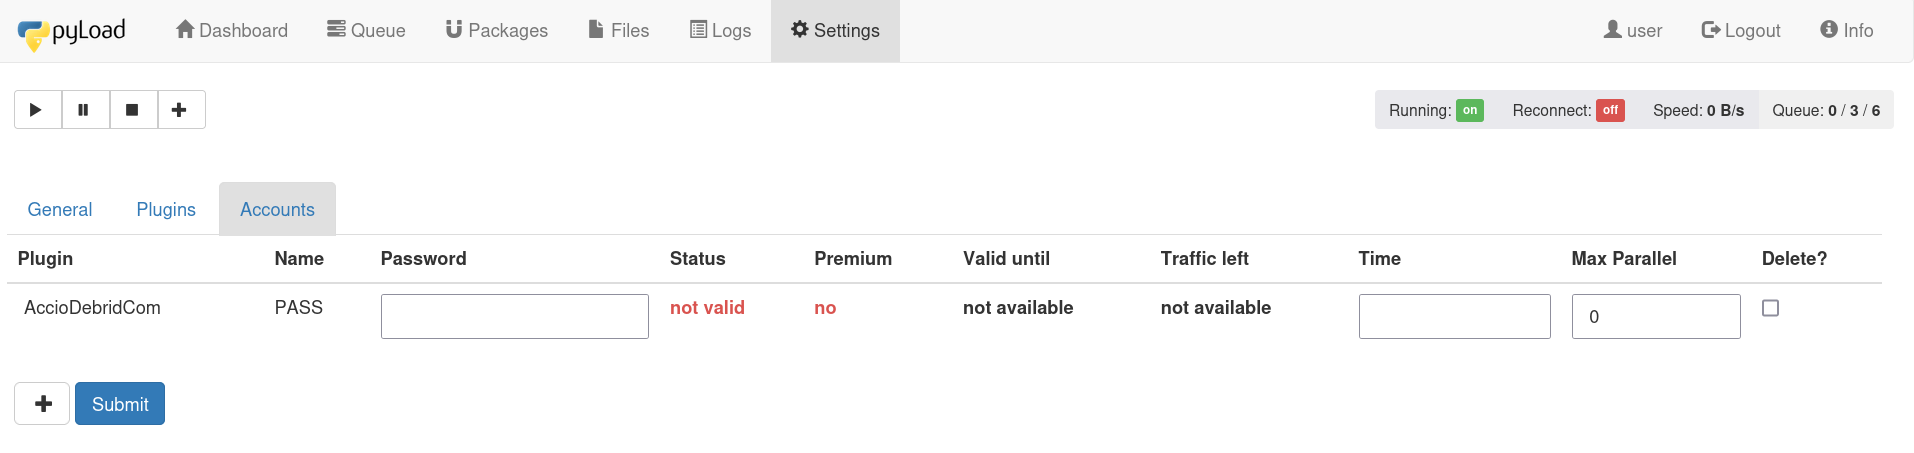
The logged in session can still be used to access everything in the application.
Impact
Should permissions be taken away, then the user is expected not to be able to execute the actions belonging to those actions anymore.
{
"affected": [
{
"package": {
"ecosystem": "PyPI",
"name": "pyload-ng"
},
"ranges": [
{
"events": [
{
"introduced": "0"
},
{
"last_affected": "0.5.0b3.dev97"
}
],
"type": "ECOSYSTEM"
}
]
}
],
"aliases": [],
"database_specific": {
"cwe_ids": [
"CWE-613"
],
"github_reviewed": true,
"github_reviewed_at": "2026-04-14T23:39:25Z",
"nvd_published_at": null,
"severity": "LOW"
},
"details": "### Summary\nThe `pyload` application does not properly invalidate or modify sessions upon changes made to a user\u0027s permissions.\n\n### Details\nWhenever an administrator changes the permissions a specific account has, they do not expect that account still being able to access data that their new permissions do not allow. This is not the case for the `pyload` application, as a user with a valid session can still perform the actions.\n\n### PoC\nTake a user with all the permissions, as shown below.\n\n\nWe now log in as this user.\n\n\nLet us now take away all the permissions.\n\n\nThe logged in session can still be used to access everything in the application.\n\n\n### Impact\nShould permissions be taken away, then the user is expected not to be able to execute the actions belonging to those actions anymore.",
"id": "GHSA-fj52-5g4h-gmq8",
"modified": "2026-04-14T23:39:25Z",
"published": "2026-04-14T23:39:25Z",
"references": [
{
"type": "WEB",
"url": "https://github.com/pyload/pyload/security/advisories/GHSA-fj52-5g4h-gmq8"
},
{
"type": "WEB",
"url": "https://github.com/pyload/pyload/commit/e95804fb0d06cbb07d2ba380fc494d9ff89b68c1"
},
{
"type": "PACKAGE",
"url": "https://github.com/pyload/pyload"
}
],
"schema_version": "1.4.0",
"severity": [
{
"score": "CVSS:4.0/AV:N/AC:H/AT:N/PR:N/UI:N/VC:L/VI:L/VA:N/SC:N/SI:N/SA:N/E:P",
"type": "CVSS_V4"
}
],
"summary": "pyLoad\u0027s Session Not Invalidated After Permission Changes"
}
GHSA-FJFH-84XH-5HV3
Vulnerability from github – Published: 2022-08-02 00:00 – Updated: 2022-08-09 00:00NLnet Labs Unbound, up to and including version 1.16.1, is vulnerable to a novel type of the "ghost domain names" attack. The vulnerability works by targeting an Unbound instance. Unbound is queried for a rogue domain name when the cached delegation information is about to expire. The rogue nameserver delays the response so that the cached delegation information is expired. Upon receiving the delayed answer containing the delegation information, Unbound overwrites the now expired entries. This action can be repeated when the delegation information is about to expire making the rogue delegation information ever-updating. From version 1.16.2 on, Unbound stores the start time for a query and uses that to decide if the cached delegation information can be overwritten.
{
  "affected": [],
  "aliases": [
    "CVE-2022-30699"
  ],
  "database_specific": {
    "cwe_ids": [
      "CWE-613"
    ],
    "github_reviewed": false,
    "github_reviewed_at": null,
    "nvd_published_at": "2022-08-01T15:15:00Z",
    "severity": "MODERATE"
  },
  "details": "NLnet Labs Unbound, up to and including version 1.16.1, is vulnerable to a novel type of the \"ghost domain names\" attack. The vulnerability works by targeting an Unbound instance. Unbound is queried for a rogue domain name when the cached delegation information is about to expire. The rogue nameserver delays the response so that the cached delegation information is expired. Upon receiving the delayed answer containing the delegation information, Unbound overwrites the now expired entries. This action can be repeated when the delegation information is about to expire making the rogue delegation information ever-updating. From version 1.16.2 on, Unbound stores the start time for a query and uses that to decide if the cached delegation information can be overwritten.",
  "id": "GHSA-fjfh-84xh-5hv3",
  "modified": "2022-08-09T00:00:27Z",
  "published": "2022-08-02T00:00:25Z",
  "references": [
    {
      "type": "ADVISORY",
      "url": "https://nvd.nist.gov/vuln/detail/CVE-2022-30699"
    },
    {
      "type": "WEB",
      "url": "https://lists.debian.org/debian-lts-announce/2023/03/msg00024.html"
    },
    {
      "type": "WEB",
      "url": "https://lists.fedoraproject.org/archives/list/package-announce@lists.fedoraproject.org/message/5L3ZFWZZFPBIL654BG75RWXUMPFQJ5EC"
    },
    {
      "type": "WEB",
      "url": "https://lists.fedoraproject.org/archives/list/package-announce@lists.fedoraproject.org/message/D35CX4SCZVNKZTWJXPDFTHWZHINMGEZD"
    },
    {
      "type": "WEB",
      "url": "https://security.gentoo.org/glsa/202212-02"
    },
    {
      "type": "WEB",
      "url": "https://www.nlnetlabs.nl/downloads/unbound/CVE-2022-30698_CVE-2022-30699.txt"
    }
  ],
  "schema_version": "1.4.0",
  "severity": [
    {
      "score": "CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:N/A:N",
      "type": "CVSS_V3"
    }
  ]
}
GHSA-FJJV-535C-93P3
Vulnerability from github – Published: 2025-07-28 21:31 – Updated: 2025-07-28 21:31Improper session invalidation in the component /bbdms/change-password.php of PHPGurukul Blood Bank & Donor Management System v2.4 allows attackers to execute a session hijacking attack.
{
  "affected": [],
  "aliases": [
    "CVE-2025-50487"
  ],
  "database_specific": {
    "cwe_ids": [
      "CWE-613"
    ],
    "github_reviewed": false,
    "github_reviewed_at": null,
    "nvd_published_at": "2025-07-28T19:15:42Z",
    "severity": "HIGH"
  },
  "details": "Improper session invalidation in the component /bbdms/change-password.php of PHPGurukul Blood Bank \u0026 Donor Management System v2.4 allows attackers to execute a session hijacking attack.",
  "id": "GHSA-fjjv-535c-93p3",
  "modified": "2025-07-28T21:31:34Z",
  "published": "2025-07-28T21:31:34Z",
  "references": [
    {
      "type": "ADVISORY",
      "url": "https://nvd.nist.gov/vuln/detail/CVE-2025-50487"
    },
    {
      "type": "WEB",
      "url": "https://github.com/VasilVK/CVE/tree/main/CVE-2025-50487"
    },
    {
      "type": "WEB",
      "url": "http://blood.com"
    },
    {
      "type": "WEB",
      "url": "http://phpgurukul.com"
    }
  ],
  "schema_version": "1.4.0",
  "severity": [
    {
      "score": "CVSS:3.1/AV:N/AC:L/PR:N/UI:R/S:U/C:H/I:L/A:N",
      "type": "CVSS_V3"
    }
  ]
}
GHSA-FMQH-2M79-343W
Vulnerability from github – Published: 2025-05-12 18:31 – Updated: 2025-05-12 18:31A suspended or recently logged-out user could continue to interact with Blueframe until the time-out period occurred.
{
  "affected": [],
  "aliases": [
    "CVE-2025-46741"
  ],
  "database_specific": {
    "cwe_ids": [
      "CWE-269",
      "CWE-613"
    ],
    "github_reviewed": false,
    "github_reviewed_at": null,
    "nvd_published_at": "2025-05-12T17:15:47Z",
    "severity": "MODERATE"
  },
  "details": "A suspended or recently logged-out user could continue to interact with Blueframe until the time-out period occurred.",
  "id": "GHSA-fmqh-2m79-343w",
  "modified": "2025-05-12T18:31:47Z",
  "published": "2025-05-12T18:31:47Z",
  "references": [
    {
      "type": "ADVISORY",
      "url": "https://nvd.nist.gov/vuln/detail/CVE-2025-46741"
    },
    {
      "type": "WEB",
      "url": "https://selinc.com/products/software/latest-software-versions"
    }
  ],
  "schema_version": "1.4.0",
  "severity": [
    {
      "score": "CVSS:3.1/AV:L/AC:H/PR:H/UI:N/S:U/C:H/I:H/A:N",
      "type": "CVSS_V3"
    }
  ]
}
GHSA-FMQW-VQH5-CWQ9
Vulnerability from github – Published: 2019-12-02 18:19 – Updated: 2021-08-19 16:03When using an authentication mechanism other than PKI, when the user clicks Log Out in NiFi versions 1.0.0 to 1.9.2, NiFi invalidates the authentication token on the client side but not on the server side. This permits the user's client-side token to be used for up to 12 hours after logging out to make API requests to NiFi.
{
  "affected": [
    {
      "package": {
        "ecosystem": "Maven",
        "name": "org.apache.nifi:nifi-web-security"
      },
      "ranges": [
        {
          "events": [
            {
              "introduced": "1.3.0"
            },
            {
              "fixed": "1.10.0"
            }
          ],
          "type": "ECOSYSTEM"
        }
      ]
    },
    {
      "package": {
        "ecosystem": "Maven",
        "name": "org.apache.nifi:nifi-web-api"
      },
      "ranges": [
        {
          "events": [
            {
              "introduced": "1.3.0"
            },
            {
              "fixed": "1.10.0"
            }
          ],
          "type": "ECOSYSTEM"
        }
      ]
    }
  ],
  "aliases": [
    "CVE-2019-12421"
  ],
  "database_specific": {
    "cwe_ids": [
      "CWE-613"
    ],
    "github_reviewed": true,
    "github_reviewed_at": "2019-12-02T17:32:47Z",
    "nvd_published_at": null,
    "severity": "HIGH"
  },
  "details": "When using an authentication mechanism other than PKI, when the user clicks Log Out in NiFi versions 1.0.0 to 1.9.2, NiFi invalidates the authentication token on the client side but not on the server side. This permits the user\u0027s client-side token to be used for up to 12 hours after logging out to make API requests to NiFi.",
  "id": "GHSA-fmqw-vqh5-cwq9",
  "modified": "2021-08-19T16:03:16Z",
  "published": "2019-12-02T18:19:39Z",
  "references": [
    {
      "type": "ADVISORY",
      "url": "https://nvd.nist.gov/vuln/detail/CVE-2019-12421"
    },
    {
      "type": "WEB",
      "url": "https://github.com/apache/nifi/pull/3362"
    },
    {
      "type": "WEB",
      "url": "https://github.com/apache/nifi/commit/cf6f5172503ce438c6c22c334c9367f774db7b24"
    },
    {
      "type": "WEB",
      "url": "https://lists.apache.org/thread.html/rca37935d661f4689cb4119f1b3b224413b22be161b678e6e6ce0c69b@%3Ccommits.nifi.apache.org%3E"
    },
    {
      "type": "WEB",
      "url": "https://nifi.apache.org/security.html#CVE-2019-12421"
    }
  ],
  "schema_version": "1.4.0",
  "severity": [
    {
      "score": "CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:H/A:H",
      "type": "CVSS_V3"
    }
  ],
  "summary": "Apache NiFi user log out issue"
}
GHSA-FP3Q-9278-8PPC
Vulnerability from github – Published: 2022-05-24 17:35 – Updated: 2022-10-02 00:00IBM Cloud Pak for Security 1.3.0.1(CP4S) does not invalidate session after logout which could allow an authenticated user to obtain sensitive information from the previous session. IBM X-Force ID: 186789.
{
  "affected": [],
  "aliases": [
    "CVE-2020-4696"
  ],
  "database_specific": {
    "cwe_ids": [
      "CWE-613"
    ],
    "github_reviewed": false,
    "github_reviewed_at": null,
    "nvd_published_at": "2020-11-30T16:15:00Z",
    "severity": "MODERATE"
  },
  "details": "IBM Cloud Pak for Security 1.3.0.1(CP4S) does not invalidate session after logout which could allow an authenticated user to obtain sensitive information from the previous session. IBM X-Force ID: 186789.",
  "id": "GHSA-fp3q-9278-8ppc",
  "modified": "2022-10-02T00:00:33Z",
  "published": "2022-05-24T17:35:19Z",
  "references": [
    {
      "type": "ADVISORY",
      "url": "https://nvd.nist.gov/vuln/detail/CVE-2020-4696"
    },
    {
      "type": "WEB",
      "url": "https://exchange.xforce.ibmcloud.com/vulnerabilities/186789"
    },
    {
      "type": "WEB",
      "url": "https://www.ibm.com/support/pages/node/6372528"
    }
  ],
  "schema_version": "1.4.0",
  "severity": [
    {
      "score": "CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:L/I:N/A:N",
      "type": "CVSS_V3"
    }
  ]
}
GHSA-FP6Q-GCCW-7QQM
Vulnerability from github – Published: 2024-10-22 17:55 – Updated: 2024-10-22 19:22Impact
The Backoffice displays the logout page with a session timeout message before the server session has fully expired, causing users to believe they have been logged out approximately 30 seconds before they actually are.
{
  "affected": [
    {
      "package": {
        "ecosystem": "NuGet",
        "name": "Umbraco.CMS"
      },
      "ranges": [
        {
          "events": [
            {
              "introduced": "13.0.0"
            },
            {
              "fixed": "13.5.2"
            }
          ],
          "type": "ECOSYSTEM"
        }
      ]
    },
    {
      "package": {
        "ecosystem": "NuGet",
        "name": "Umbraco.CMS"
      },
      "ranges": [
        {
          "events": [
            {
              "introduced": "10.0.0"
            },
            {
              "fixed": "10.8.7"
            }
          ],
          "type": "ECOSYSTEM"
        }
      ]
    },
    {
      "package": {
        "ecosystem": "NuGet",
        "name": "UmbracoCMS"
      },
      "ranges": [
        {
          "events": [
            {
              "introduced": "8.0.0"
            },
            {
              "fixed": "8.18.15"
            }
          ],
          "type": "ECOSYSTEM"
        }
      ]
    }
  ],
  "aliases": [
    "CVE-2024-48926"
  ],
  "database_specific": {
    "cwe_ids": [
      "CWE-613"
    ],
    "github_reviewed": true,
    "github_reviewed_at": "2024-10-22T17:55:01Z",
    "nvd_published_at": "2024-10-22T16:15:08Z",
    "severity": "MODERATE"
  },
  "details": "### Impact\nThe Backoffice displays the logout page with a session timeout message before the server session has fully expired, causing users to believe they have been logged out approximately 30 seconds before they actually are.\n",
  "id": "GHSA-fp6q-gccw-7qqm",
  "modified": "2024-10-22T19:22:29Z",
  "published": "2024-10-22T17:55:01Z",
  "references": [
    {
      "type": "WEB",
      "url": "https://github.com/umbraco/Umbraco-CMS/security/advisories/GHSA-fp6q-gccw-7qqm"
    },
    {
      "type": "ADVISORY",
      "url": "https://nvd.nist.gov/vuln/detail/CVE-2024-48926"
    },
    {
      "type": "PACKAGE",
      "url": "https://github.com/umbraco/Umbraco-CMS"
    }
  ],
  "schema_version": "1.4.0",
  "severity": [
    {
      "score": "CVSS:3.1/AV:N/AC:H/PR:N/UI:R/S:U/C:L/I:L/A:N",
      "type": "CVSS_V3"
    }
  ],
  "summary": "Umbraco CMS logout page displayed before session expiration"
}
GHSA-FPCR-4RR5-HPCP
Vulnerability from github – Published: 2022-05-24 17:21 – Updated: 2026-02-10 14:16An issue was discovered in Mattermost Server before 4.0.0, 3.10.2, and 3.9.2, when Single Sign-On OAuth2 is used. An attacker could claim somebody else's account.
{
  "affected": [
    {
      "package": {
        "ecosystem": "Go",
        "name": "github.com/mattermost/mattermost-server"
      },
      "ranges": [
        {
          "events": [
            {
              "introduced": "0"
            },
            {
              "fixed": "3.9.2-0.20170714134023-b17fca0d5ee7"
            }
          ],
          "type": "ECOSYSTEM"
        }
      ]
    },
    {
      "package": {
        "ecosystem": "Go",
        "name": "github.com/mattermost/mattermost-server"
      },
      "ranges": [
        {
          "events": [
            {
              "introduced": "3.10.0"
            },
            {
              "fixed": "3.10.2"
            }
          ],
          "type": "ECOSYSTEM"
        }
      ]
    }
  ],
  "aliases": [
    "CVE-2017-18906"
  ],
  "database_specific": {
    "cwe_ids": [
      "CWE-613"
    ],
    "github_reviewed": true,
    "github_reviewed_at": "2026-02-06T22:42:23Z",
    "nvd_published_at": "2020-06-19T20:15:00Z",
    "severity": "HIGH"
  },
  "details": "An issue was discovered in Mattermost Server before 4.0.0, 3.10.2, and 3.9.2, when Single Sign-On OAuth2 is used. An attacker could claim somebody else\u0027s account.",
  "id": "GHSA-fpcr-4rr5-hpcp",
  "modified": "2026-02-10T14:16:10Z",
  "published": "2022-05-24T17:21:06Z",
  "references": [
    {
      "type": "ADVISORY",
      "url": "https://nvd.nist.gov/vuln/detail/CVE-2017-18906"
    },
    {
      "type": "WEB",
      "url": "https://github.com/mattermost/mattermost/commit/259ad46f30d0fac2f7c5c14f3b76b2170f7e90c7"
    },
    {
      "type": "WEB",
      "url": "https://github.com/mattermost/mattermost/commit/b17fca0d5ee7557e3df1cf1d1da8bd749859e35f"
    },
    {
      "type": "WEB",
      "url": "https://github.com/mattermost/mattermost/commit/fbc170733e86f09b46ba754dd03304733d2f482f"
    },
    {
      "type": "PACKAGE",
      "url": "https://github.com/mattermost/mattermost"
    },
    {
      "type": "WEB",
      "url": "https://mattermost.com/security-updates"
    }
  ],
  "schema_version": "1.4.0",
  "severity": [
    {
      "score": "CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:H/A:N",
      "type": "CVSS_V3"
    }
  ],
  "summary": "Mattermost Server vulnerable to user account takeover when Single Sign-On OAuth2 is used"
}
Mitigation
Set sessions/credentials expiration date.
No CAPEC attack patterns related to this CWE.